A Roadmap to
Sustainable Compliance

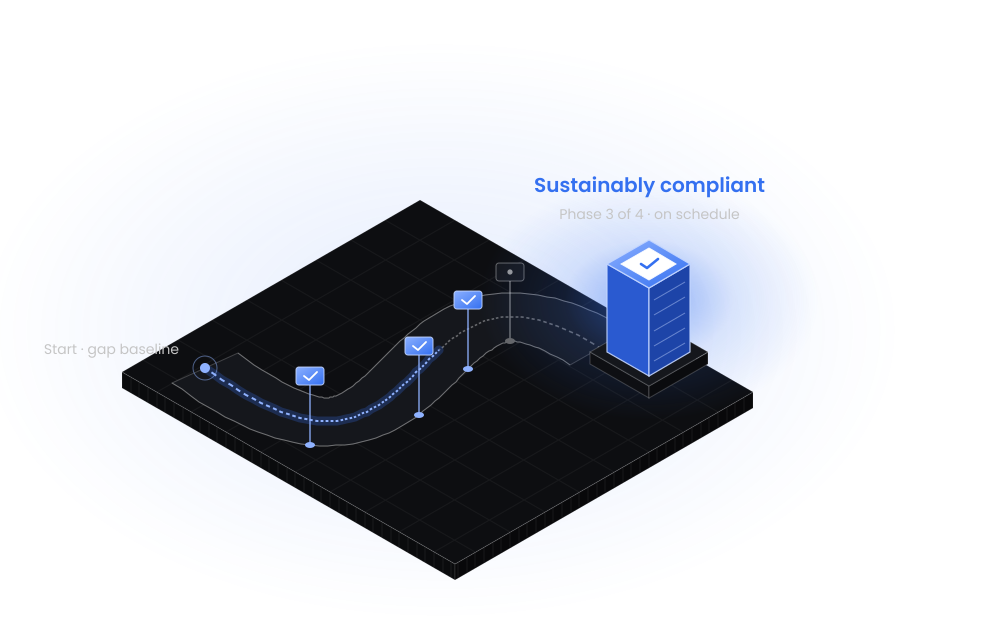
A tailored compliance strategy mapped to business goals and regulatory requirements, with a phased remediation plan and clear milestones.

Trusted by fastest growing
companies around the world.

American Airlines logo
Centene Corporation logo
Intrado logo
NTT Data logo
Pfizer logo
FAB logo
Anheuser-Busch InBev logo
CBCInnovis logo
JCPenney logo
OU Health logo
Protegrity logo
Blue Cross Blue Shield logo
Dell Technologies logo
Lumen logo
P&G logo
nCipher logo
Builders FirstSource logo
Intel logo
Magella Health logo
Pega logo
LivaNova logo

Why Compliance Strategy?

One Strategy for Every Framework You Answer To

A step-by-step plan that turns your gaps into milestones, aligned to the frameworks that apply to you.

Strategy and Roadmap illustration

Strategy and Roadmap

Develop a comprehensive strategy and remediation roadmap for each identified gap in your cryptographic controls.

Unified Compliance illustration

Unified Compliance

Address PCI DSS, NIST CSF, FIPS 140-3, DORA, NIS2, HIPAA, and GDPR through one unified roadmap for your team.

Regulatory Monitoring illustration

Regulatory Monitoring

Get proactive updates as NIST, PCI DSS, DORA, and NIS2 requirements evolve, through continuous monitoring.

Scope

Five Domains, One Strategy

Action-driven roadmaps that help you meet critical compliance requirements and strengthen your security posture.

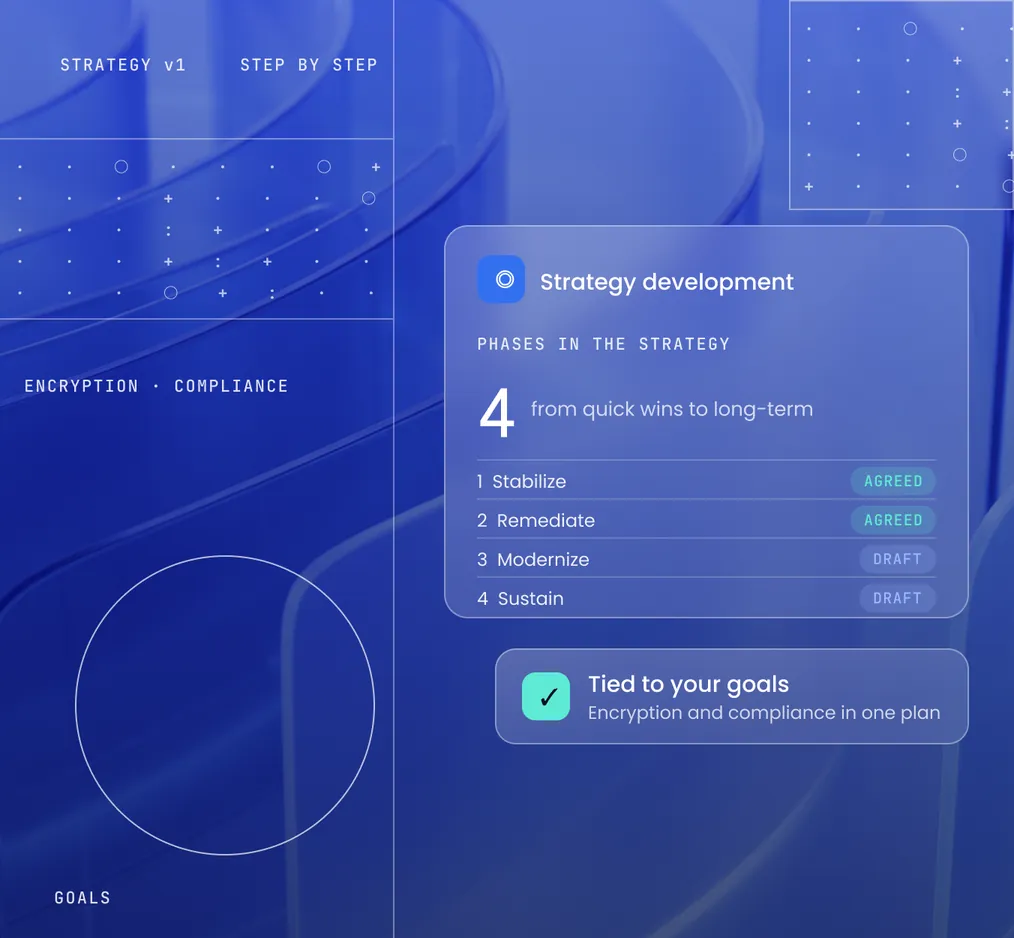
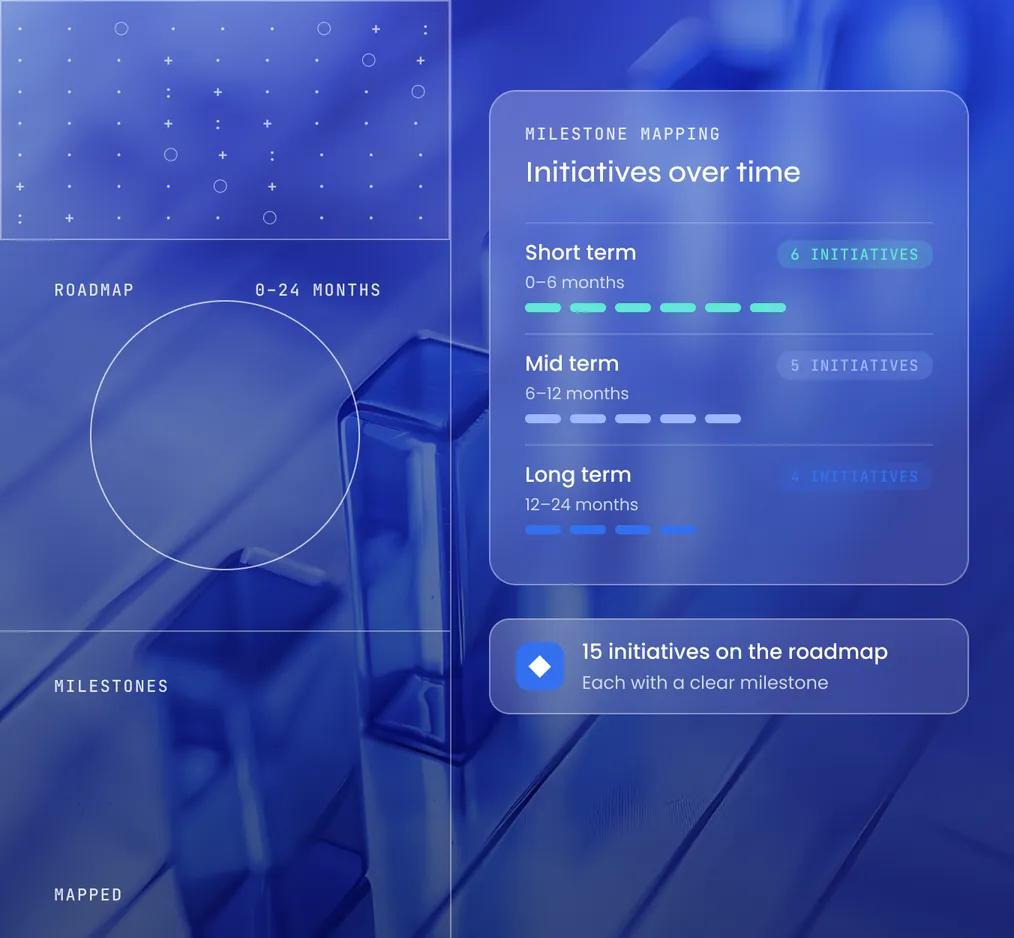
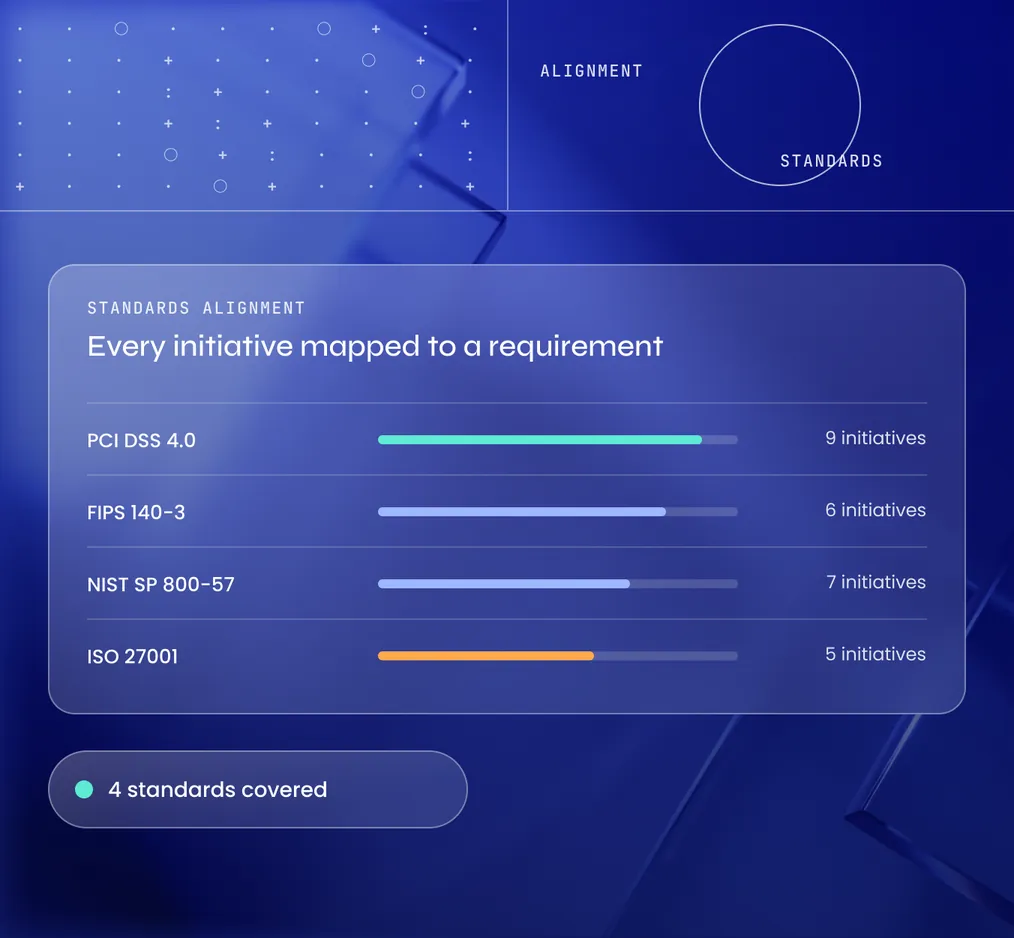
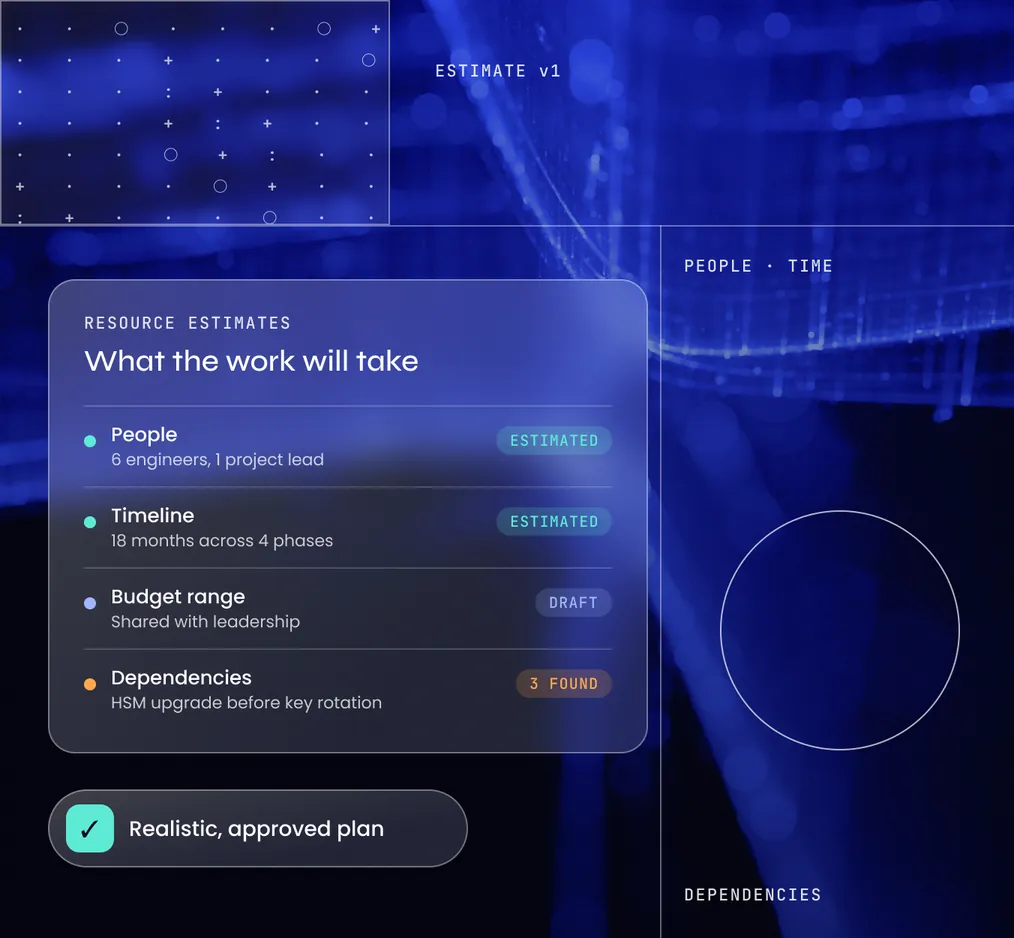
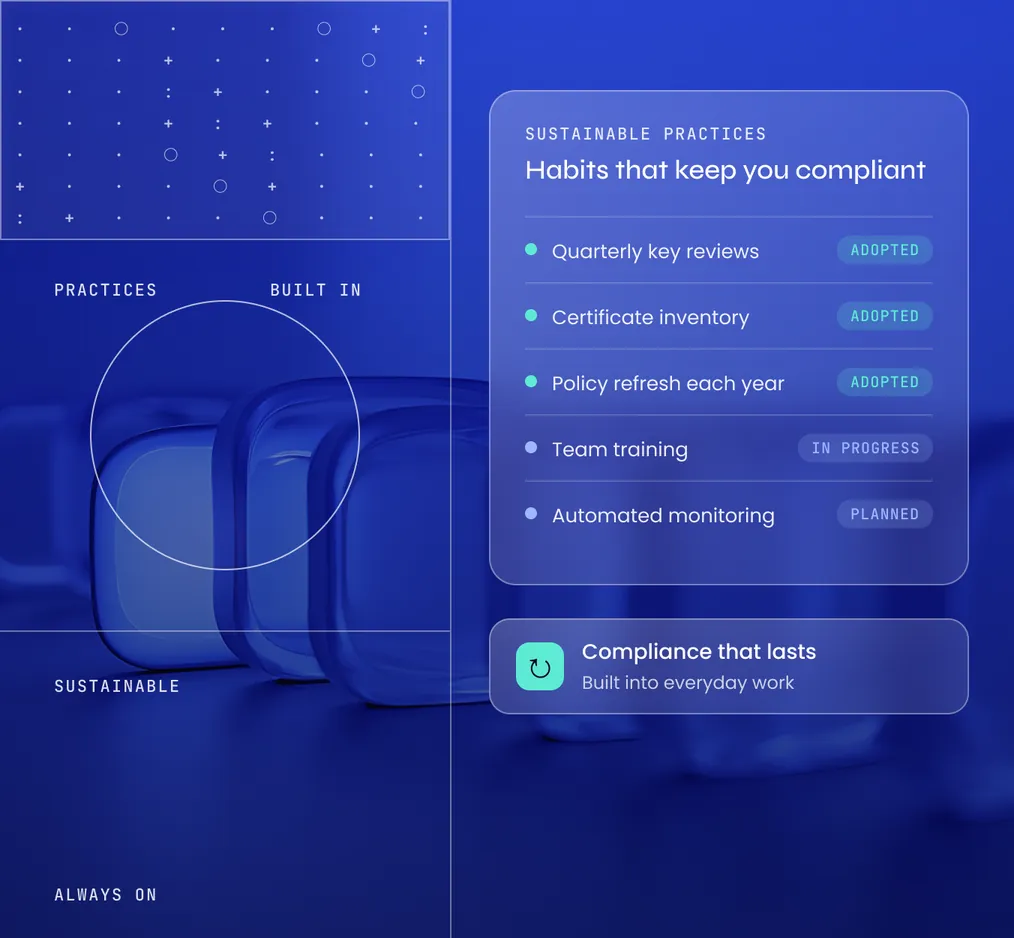
Strategy Development Milestone Mapping Standards Alignment Resource Estimates Sustainable Practices
  1. Build a step-by-step strategy for your encryption and compliance goals.

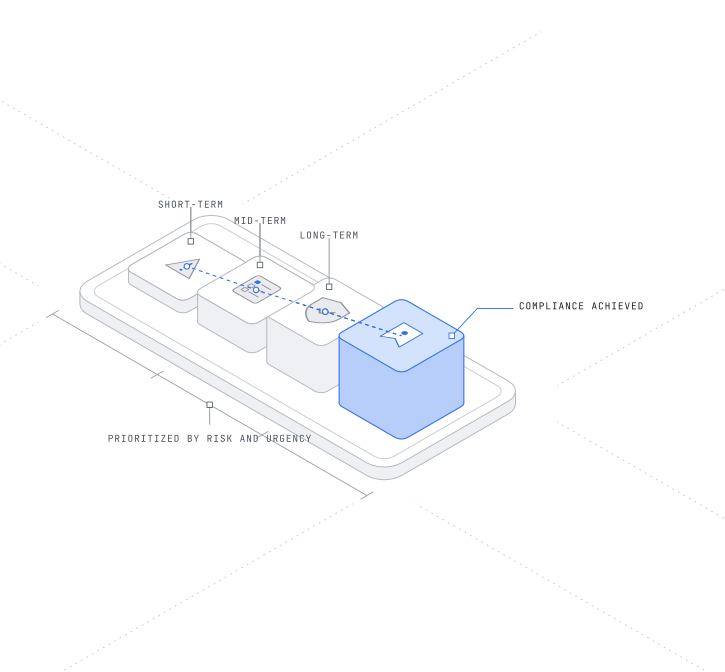
  2. Map remediation initiatives to short-term and long-term milestones.

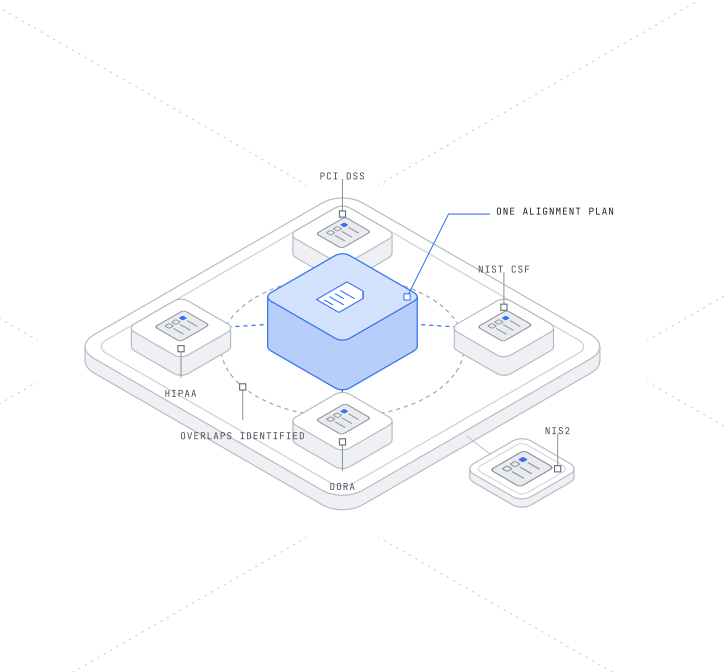
  3. Align roadmap initiatives with compliance requirements and standards.

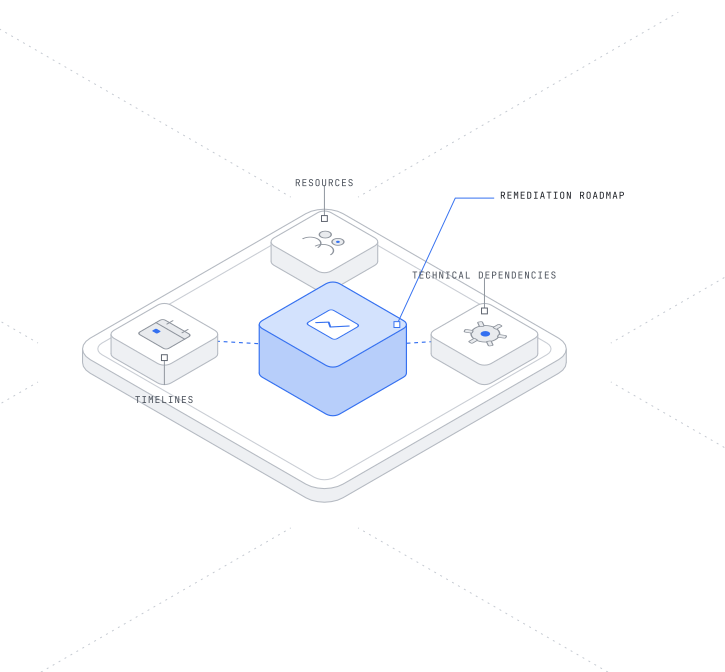
  4. Estimate resources, timelines, and technical dependencies for the work.

  5. Guide your team in adopting best practices for sustainable compliance.

Our Approach

Four Pillars of Your Compliance Strategy

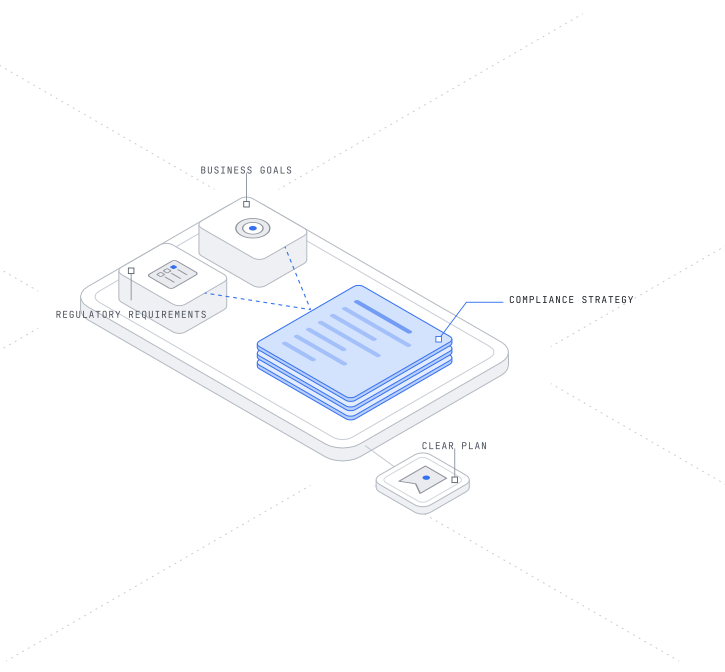
Every strategy is built around your business goals, your regulatory requirements, and the resources you actually have.

  1. Tailored Strategy

    Built Around Your Business

    Build a tailored compliance strategy mapped to your business goals and regulatory requirements, with a clear plan.

    • Mapped to your own business objectives
    • Mapped to your regulatory requirements
    • Strategy document for lasting compliance
    Talk to an Advisor
    Built Around Your Business
  2. Phased Remediation

    Sequence the Fixes

    Develop a phased remediation plan with short-term and long-term milestones for closing each of your compliance gaps.

    • Short-term and long-term milestones set
    • Gaps prioritized by risk and urgency
    • Step-by-step roadmap for compliance
    Talk to an Advisor
    Sequence the Fixes
  3. Resource Planning

    Know What It Will Take

    Estimate the resources, timelines, and technical dependencies your team needs to carry out the remediation roadmap.

    • Resource requirements estimated early
    • Timelines estimated for each phase
    • Technical dependencies identified upfront
    Talk to an Advisor
    Know What It Will Take
  4. Framework Alignment

    One Plan, Many Frameworks

    Create an alignment plan with frameworks like PCI DSS, NIST CSF, HIPAA, DORA, and NIS2 that covers overlaps.

    • Alignment with PCI DSS, NIST CSF, DORA
    • Overlaps between frameworks identified
    • Duplication of effort reduced for teams
    Talk to an Advisor
    One Plan, Many Frameworks

Next Steps

Where the Strategy Leads Next

The strategy gives you a clear, phased roadmap, and implementation puts it into practice.

FAQs

Frequently Asked Questions

Still have questions? Talk to our team

Plan Your
Strategy

Tell us about your environment and deadlines, and we will come back with a roadmap, a timeline and a team.

Plan Your Strategy