Put Your Compliance Plan
Into Practice

Implementation planning and support, plus guided transitions to updated standards such as FIPS 140-3, with minimal disruption.

Trusted by fastest growing
companies around the world.

American Airlines logo
Centene Corporation logo
Intrado logo
NTT Data logo
Pfizer logo
FAB logo
Anheuser-Busch InBev logo
CBCInnovis logo
JCPenney logo
OU Health logo
Protegrity logo
Blue Cross Blue Shield logo
Dell Technologies logo
Lumen logo
P&G logo
nCipher logo
Builders FirstSource logo
Intel logo
Magella Health logo
Pega logo
LivaNova logo

Why Compliance Implementation?

Close Your Gaps Without Disrupting the Business

A clear plan, guidance for minimal disruption, and support that continues as regulations change.

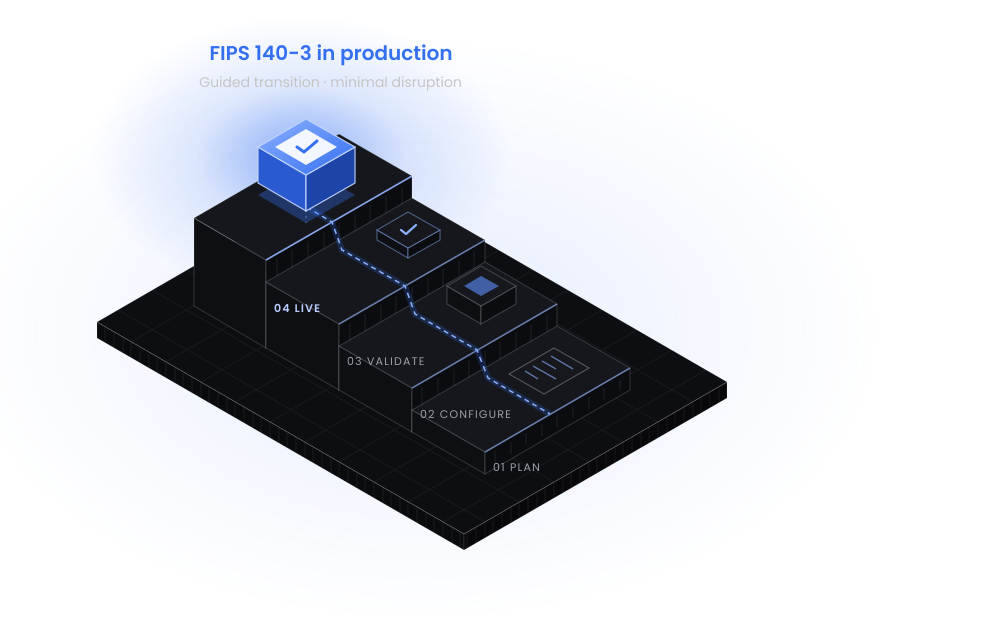
FIPS 140-3 Transition illustration

FIPS 140-3 Transition

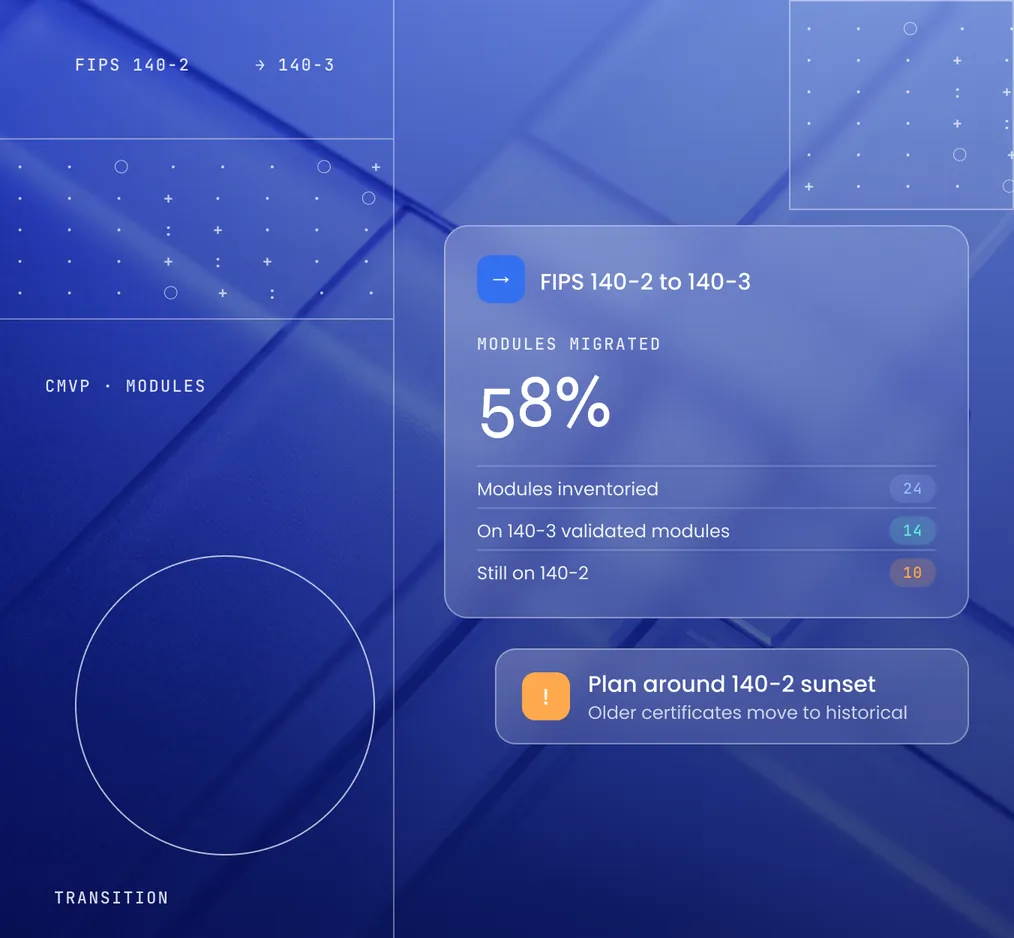
Get full end-to-end advice on moving from FIPS 140-2 to FIPS 140-3, ideal for federal contractors.

Risk Mitigation illustration

Risk Mitigation

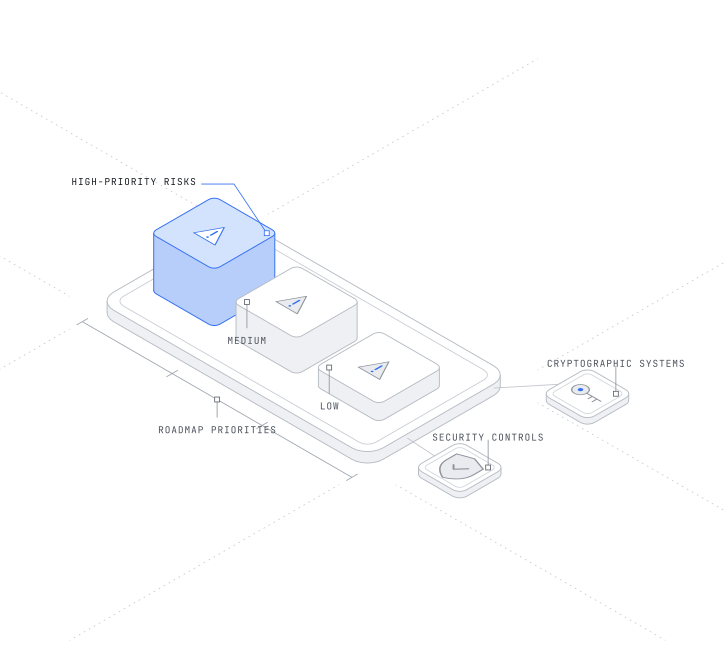
Address high-priority compliance risks within your cryptographic systems and security controls first.

Ongoing Support illustration

Ongoing Support

Receive continuous guidance, updates, and maintenance to sustain compliance with minimal disruption.

Scope

Five Domains, One Implementation

Support for putting your compliance plan into practice and moving to updated standards.

Implementation Plan Compliance Transition Setup Review Policy Alignment Validation Support
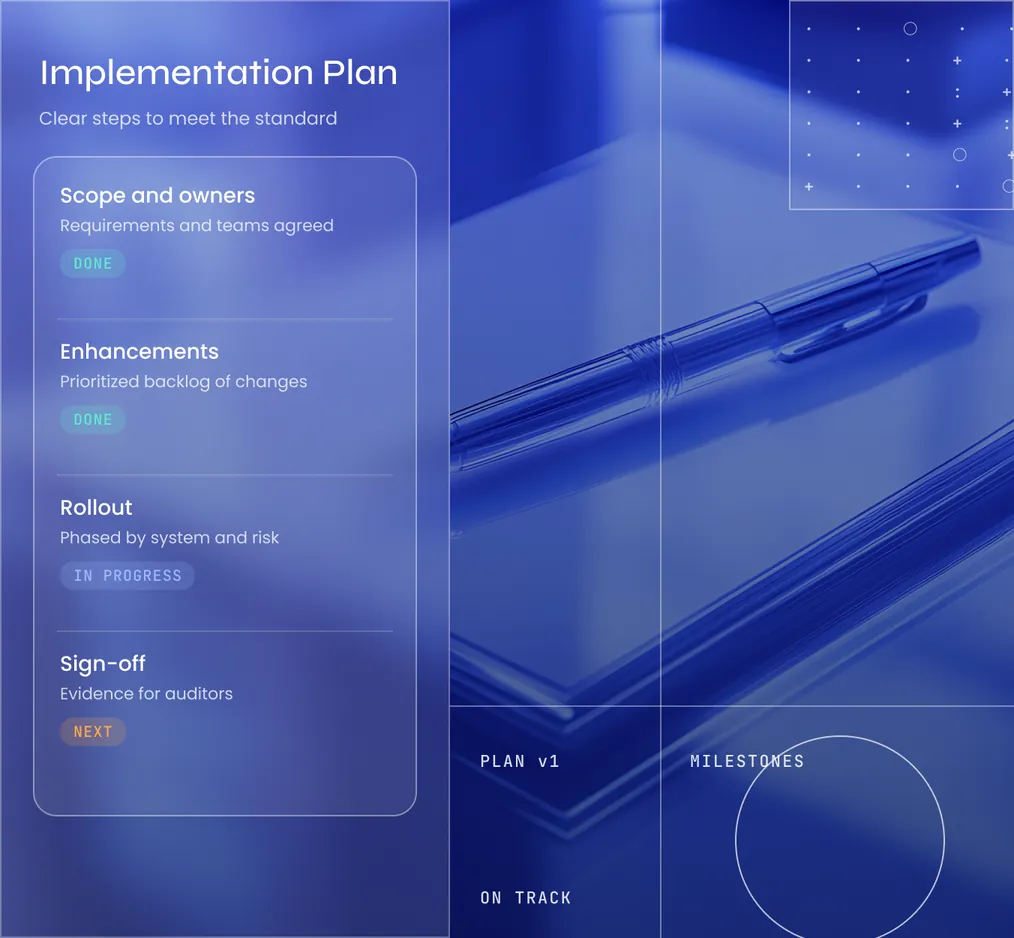
  1. Set a clear plan for implementing enhancements and meeting requirements.

  2. Support migration to updated standards, such as FIPS 140-2 to 140-3.

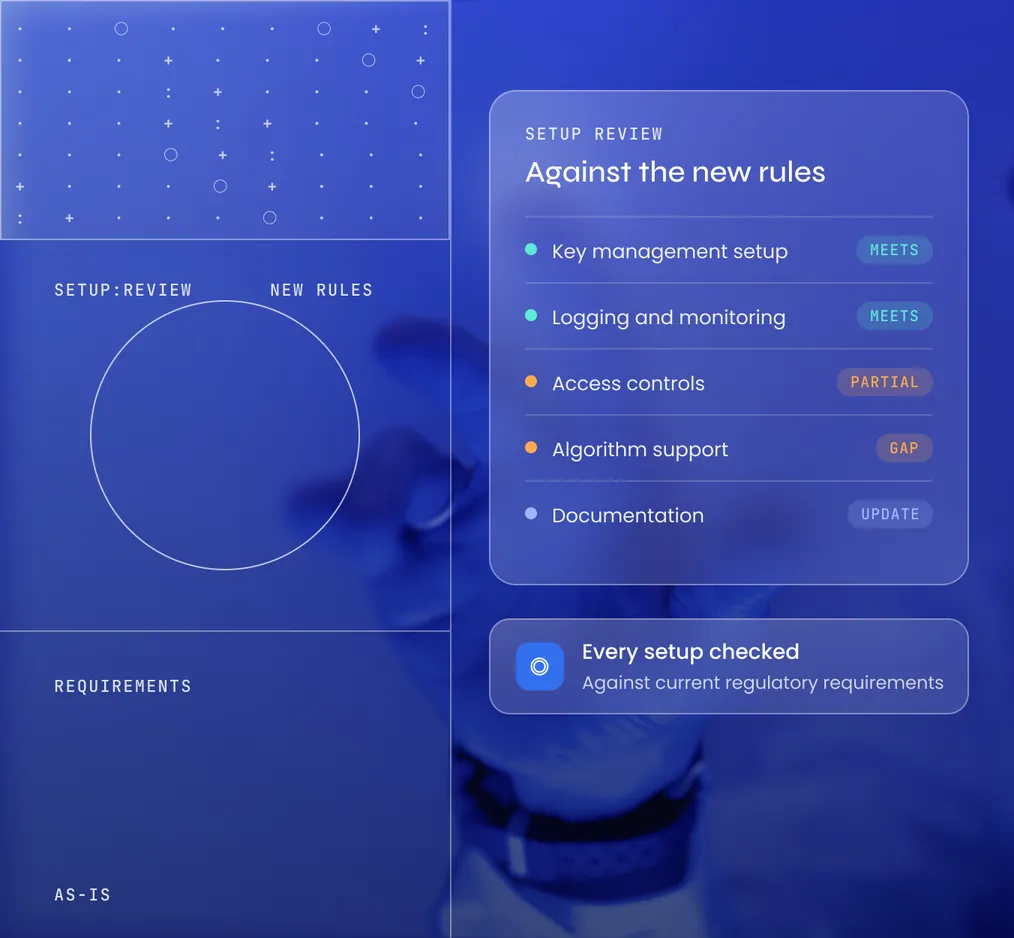
  3. Review existing compliance setups against new regulatory requirements.

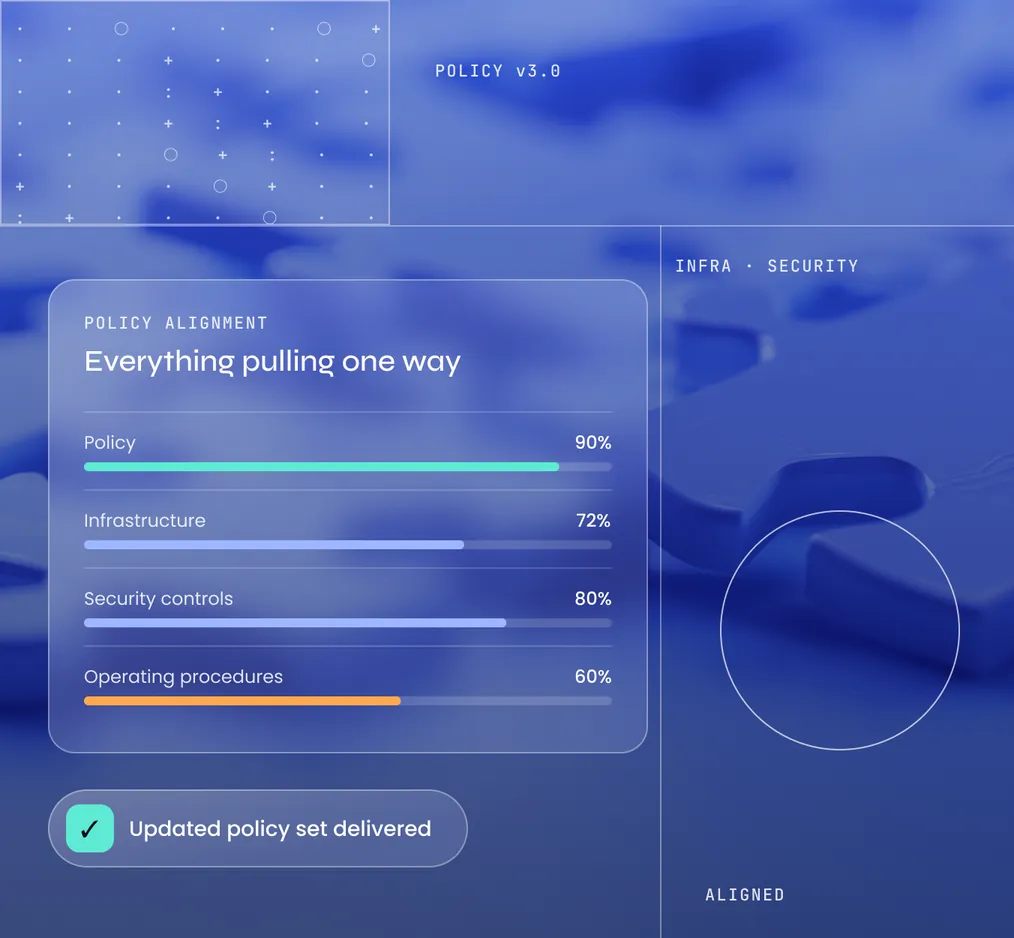
  4. Provide updated policy, infrastructure, and security alignment advice.

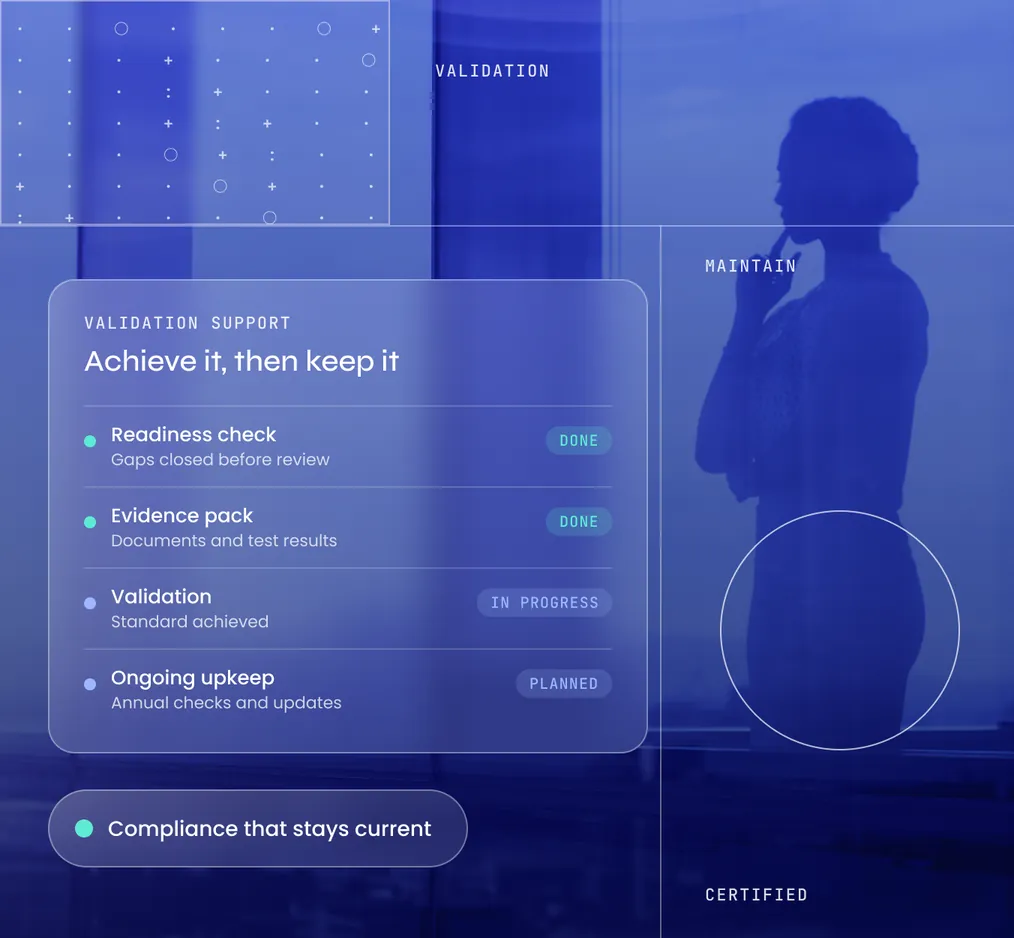
  5. Help your team achieve and then maintain the new compliance standard.

Our Approach

Four Pillars of Your Compliance Implementation

Planning, transition support, risk mitigation, and adaptation, so your compliance stays in place after the work is done.

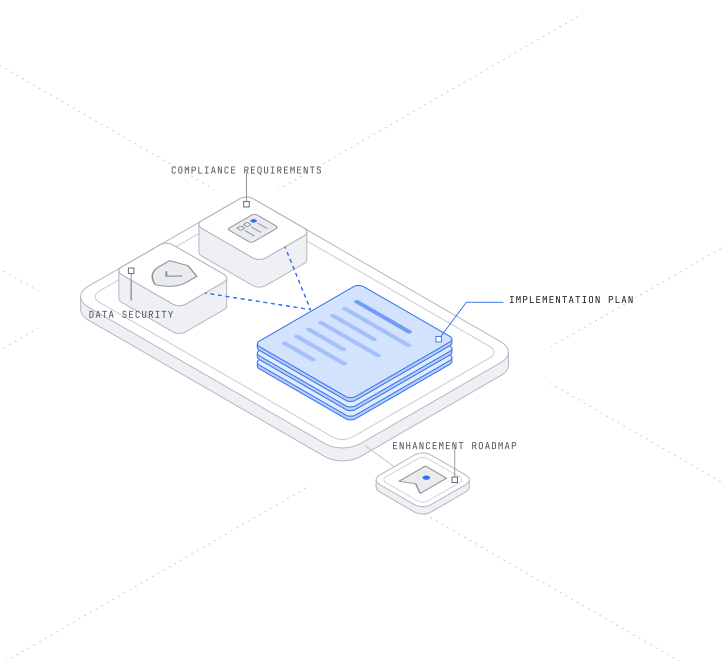
  1. Implementation Planning

    Plan the Work, Then Support It

    Establish a clear plan for implementing enhancements, aligning with compliance requirements, and strengthening data security.

    • A clear implementation plan in place
    • Aligned with your compliance requirements
    • A stronger data security environment
    Talk to an Advisor
    Plan the Work, Then Support It
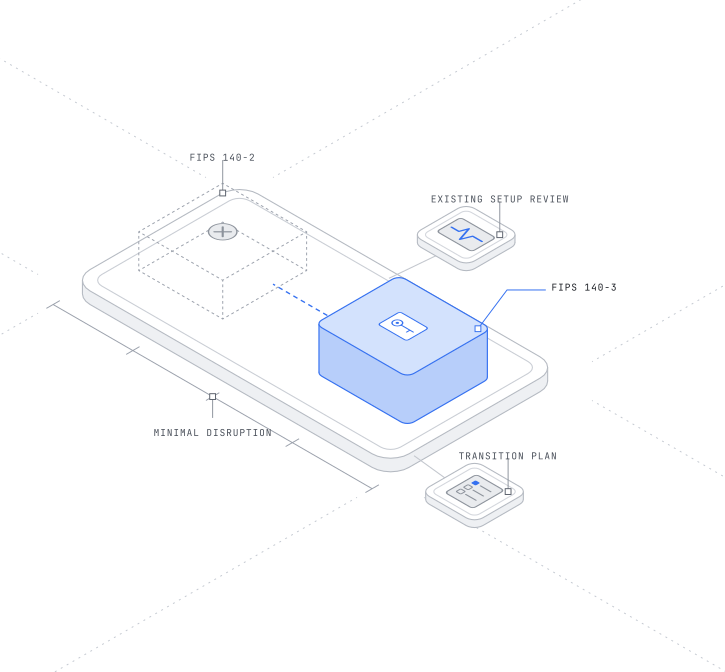
  2. Compliance Transition

    Move to the New Standard

    Support migration to updated compliance standards, such as FIPS 140-2 to FIPS 140-3, with guidance for minimal disruption.

    • Existing setup reviewed against new rules
    • Guidance for minimal disruption given
    • Transition plan for new compliance mandates
    Talk to an Advisor
    Move to the New Standard
  3. Risk Mitigation

    Close the Highest Risks First

    Address high-priority compliance risks within your cryptographic systems and security controls, following your roadmap priorities.

    • High-priority risks addressed first
    • Cryptographic systems and controls covered
    • Aligned with your remediation roadmap
    Talk to an Advisor
    Close the Highest Risks First
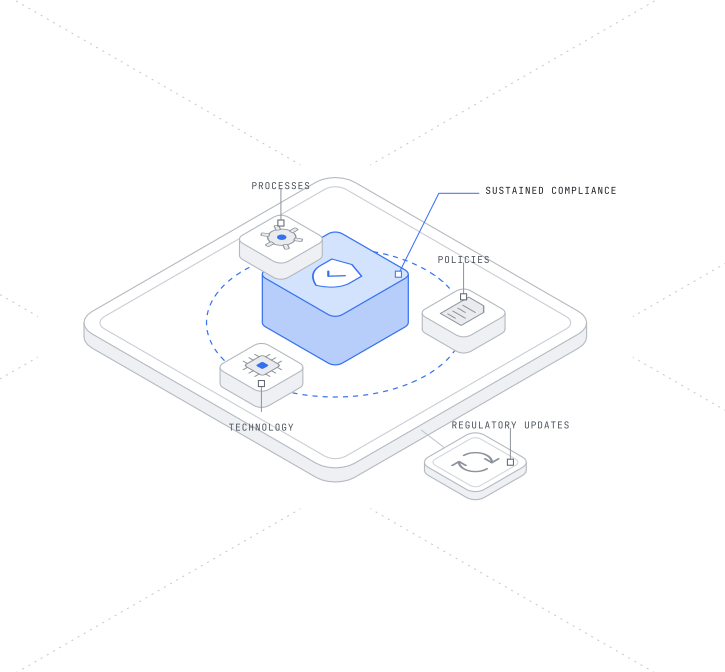
  4. Regulatory Adaptation

    Stay Aligned as Rules Change

    Maintain alignment with changing regulations by adapting your processes, policies, and technologies as requirements evolve.

    • Processes, policies, and technology adapted
    • Regulatory updates monitored continuously
    • Ongoing support to sustain compliance
    Talk to an Advisor
    Stay Aligned as Rules Change

Next Steps

Where the Implementation Leads Next

Implementation puts your plan into practice, and ongoing advisory keeps your compliance current.

FAQs

Frequently Asked Questions

Still have questions? Talk to our team

Plan Your
Implementation

Tell us about your environment and deadlines, and we will come back with a plan, a timeline and a team.

Plan Your Implementation