Prove Your
Encryption Holds Up

An independent audit of your encryption controls, key management and compliance, mapped to NIST, GDPR, HIPAA and PCI DSS.

Trusted by fastest growing
companies around the world.

American Airlines logo
Centene Corporation logo
Intrado logo
NTT Data logo
Pfizer logo
FAB logo
Anheuser-Busch InBev logo
CBCInnovis logo
JCPenney logo
OU Health logo
Protegrity logo
Blue Cross Blue Shield logo
Dell Technologies logo
Lumen logo
P&G logo
nCipher logo
Builders FirstSource logo
Intel logo
Magella Health logo
Pega logo
LivaNova logo

Why Encryption Audit?

Independent Proof of Your Encryption Posture

A third-party view of your controls, configurations, and compliance, with prioritized steps to fix what it finds.

Complete Environment Visibility illustration

Complete Environment Visibility

Get an in-depth review of your entire encryption ecosystem, including controls, configurations, and key usage.

Actionable Audit Reports illustration

Actionable Audit Reports

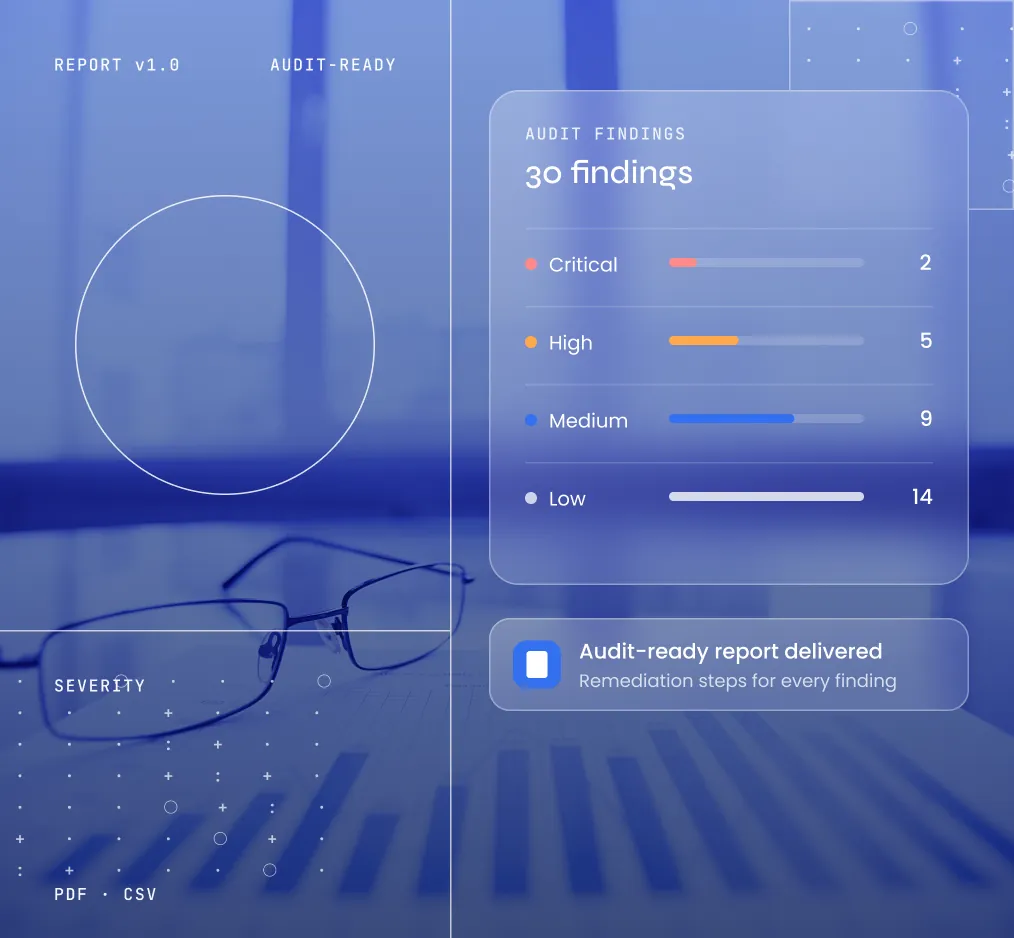
Receive detailed findings with prioritized remediation steps and risk scores aligned to business impact for your team.

Compliance Validation illustration

Compliance Validation

Ensure your encryption practices meet NIST, GDPR, PCI DSS, HIPAA, and other evolving regulatory frameworks over time.

Scope

Five Domains, One Audit

We conduct independent audits to verify encryption control effectiveness, policy adherence, and regulatory compliance across your organization.

Audit Planning Data Collection Control Assessment Compliance Review Findings Report
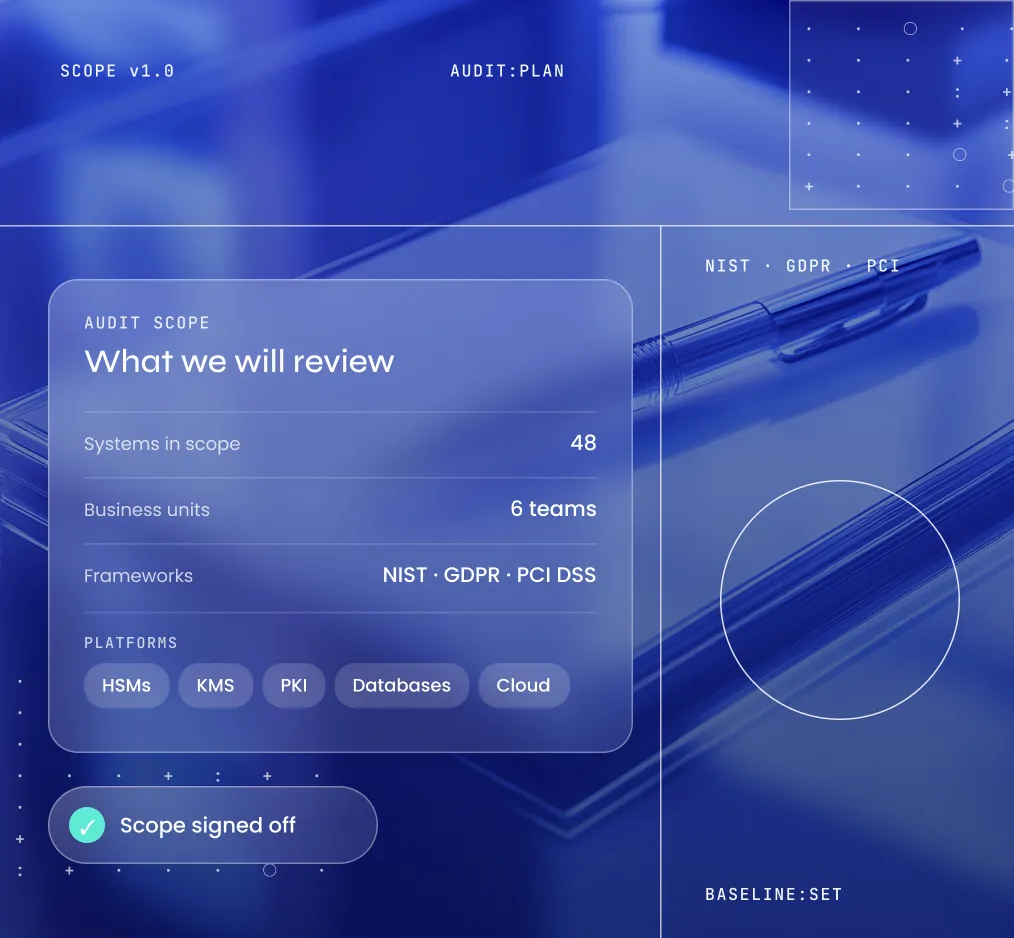
  1. Define scope, systems, and compliance goals for an efficient, targeted review.

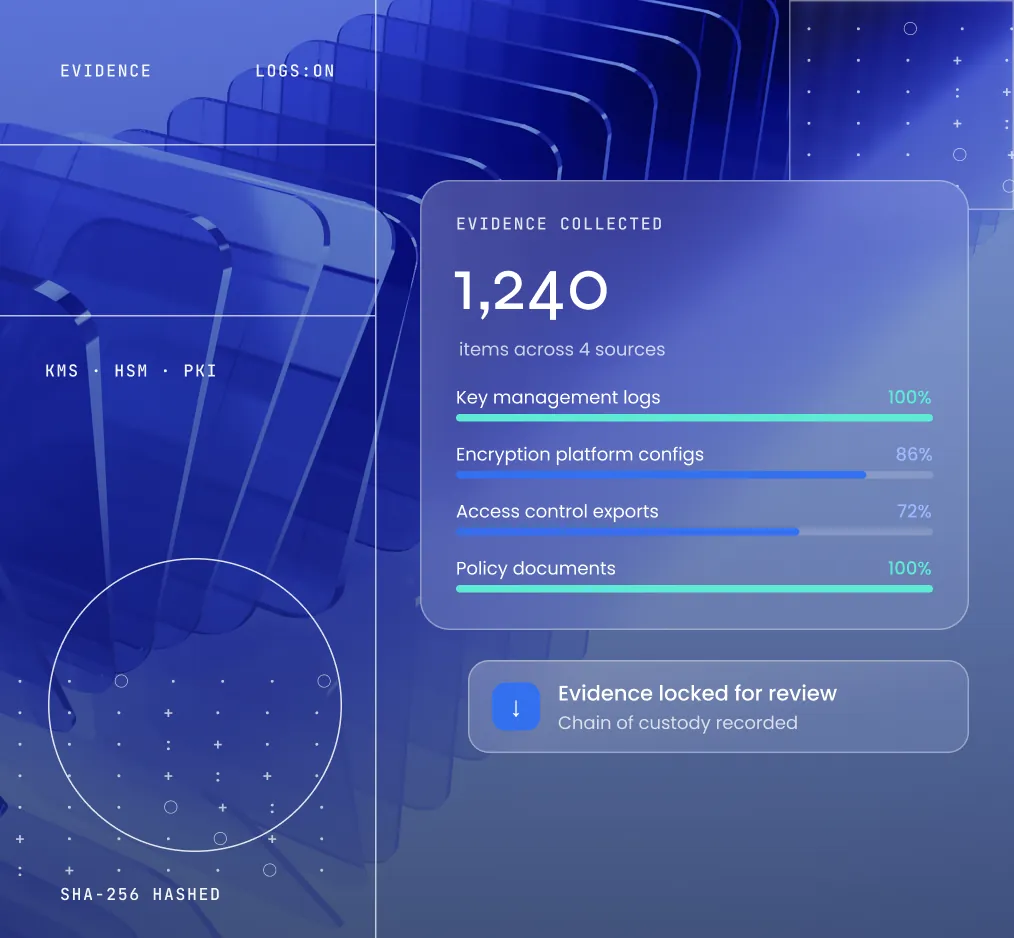
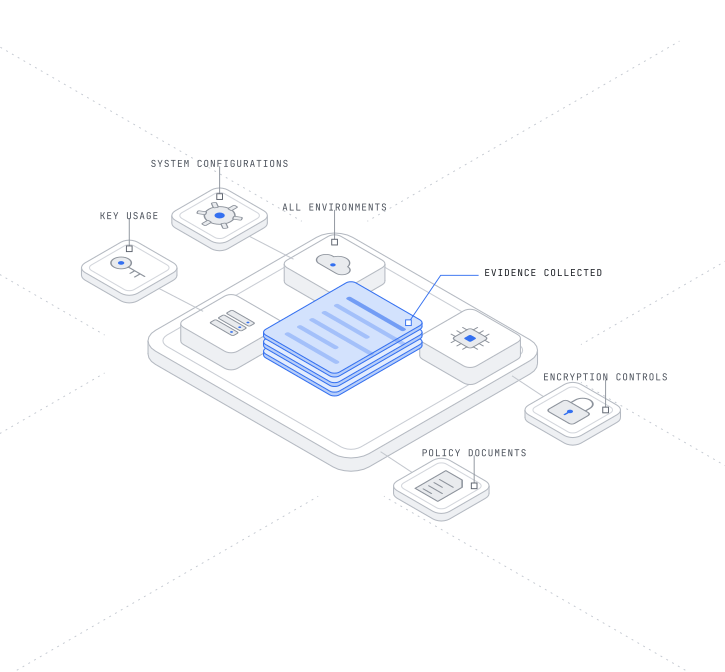
  2. Gather evidence from key management, encryption platforms, and security controls.

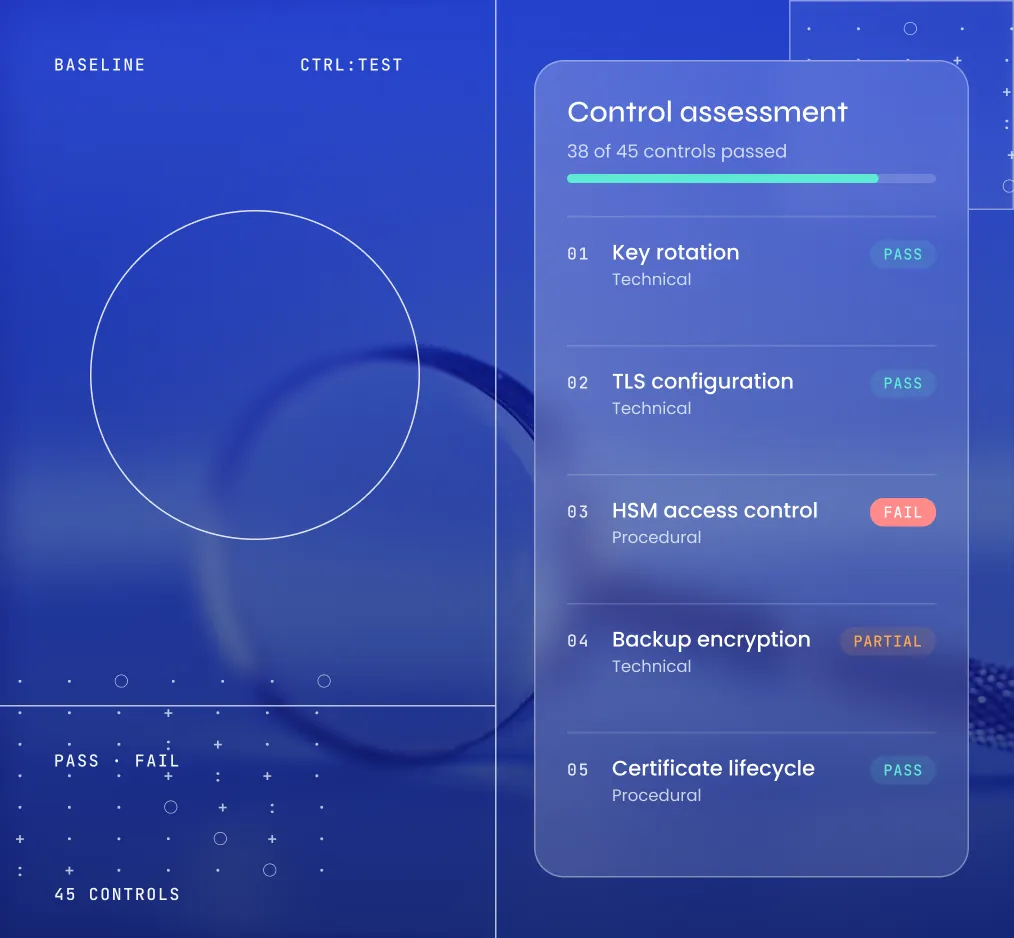
  3. Assess technical and procedural safeguards against defined encryption baselines.

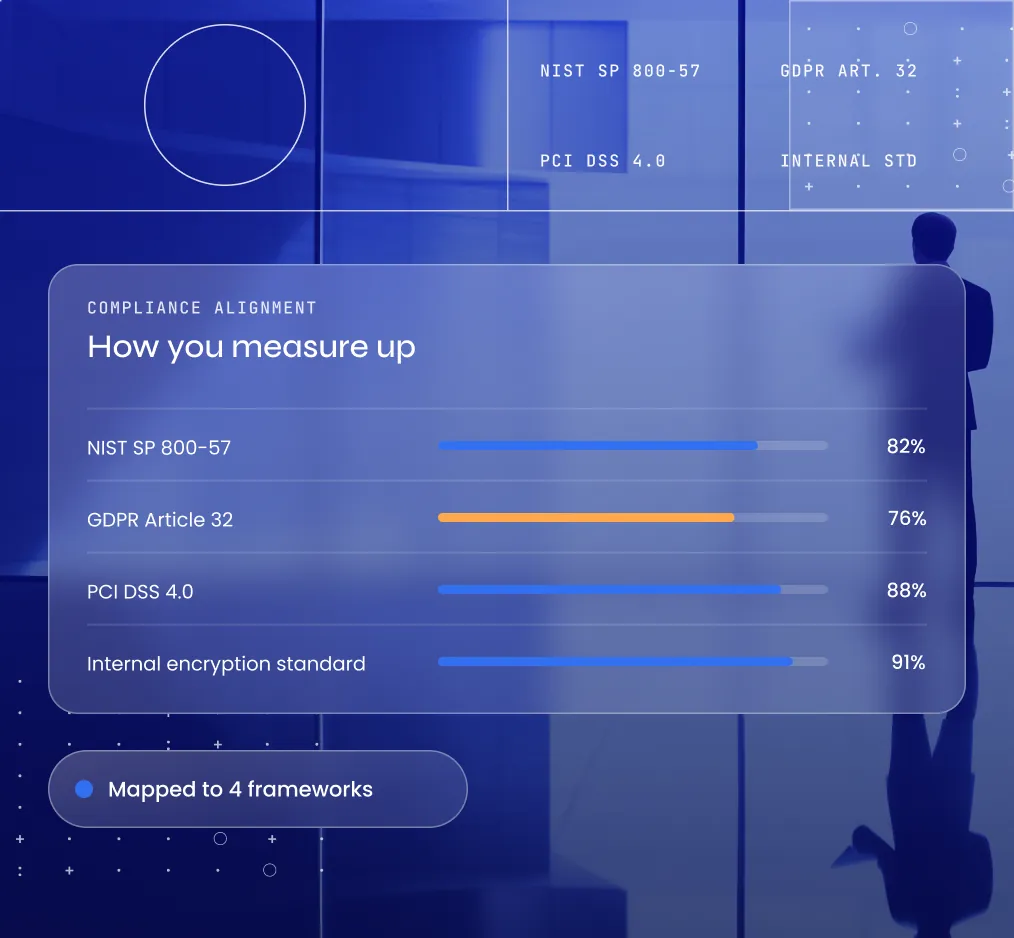
  4. Evaluate alignment with internal standards and external mandates like NIST, GDPR.

  5. Deliver actionable insights with severity ratings and audit-ready documentation.

Our Approach

Four Pillars of Your Audit

Independent verification of encryption posture with clear insights into configuration flaws, policy gaps, and compliance misalignments.

  1. Comprehensive Data Collection

    Collect the Evidence

    Review system configurations, key usage, encryption controls, and policy documents across all relevant platforms and environments.

    • System configurations and key usage reviewed
    • Encryption controls and policies examined
    • All relevant platforms and environments covered
    Talk to an Advisor
    Collect the Evidence
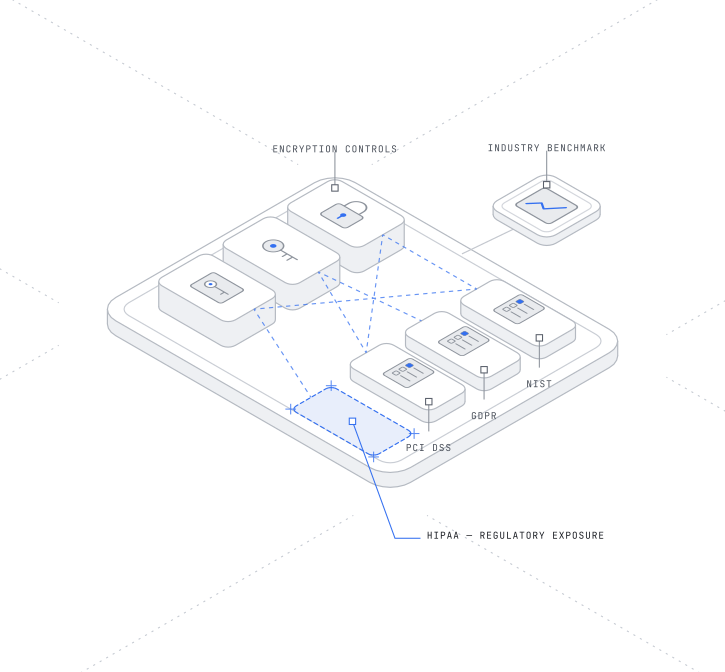
  2. Regulatory Control Mapping

    Map Controls to Regulations

    Assess your adherence to NIST, GDPR, PCI DSS, HIPAA, and other frameworks using a structured control mapping methodology.

    • Structured control mapping methodology used
    • Program benchmarked against industry standards
    • Regulatory exposure uncovered for your team
    Talk to an Advisor
    Map Controls to Regulations
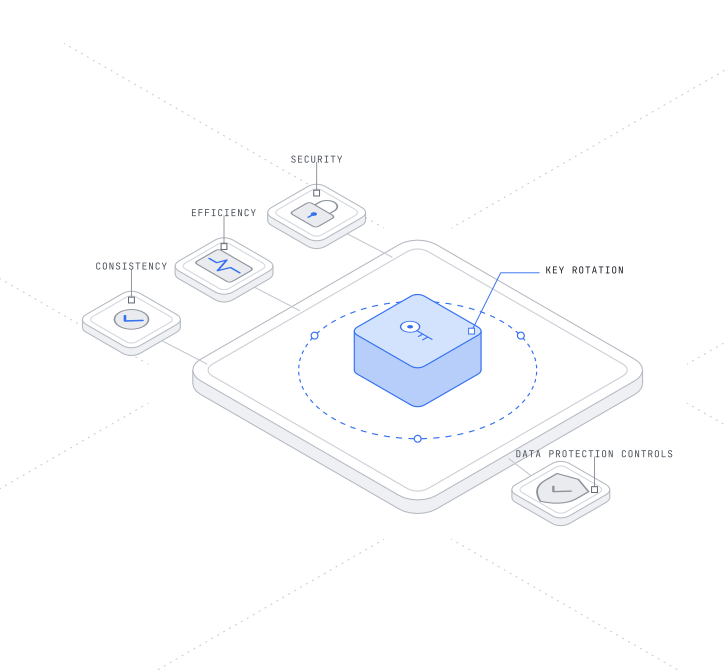
  3. Encryption Practice Review

    Review How Encryption Is Run

    Evaluate the security, efficiency, and consistency of encryption mechanisms, including key rotation and data protection controls.

    • Security, efficiency, and consistency evaluated
    • Key rotation and data protection reviewed
    • Robustness of encryption operations assessed
    Talk to an Advisor
    Review How Encryption Is Run
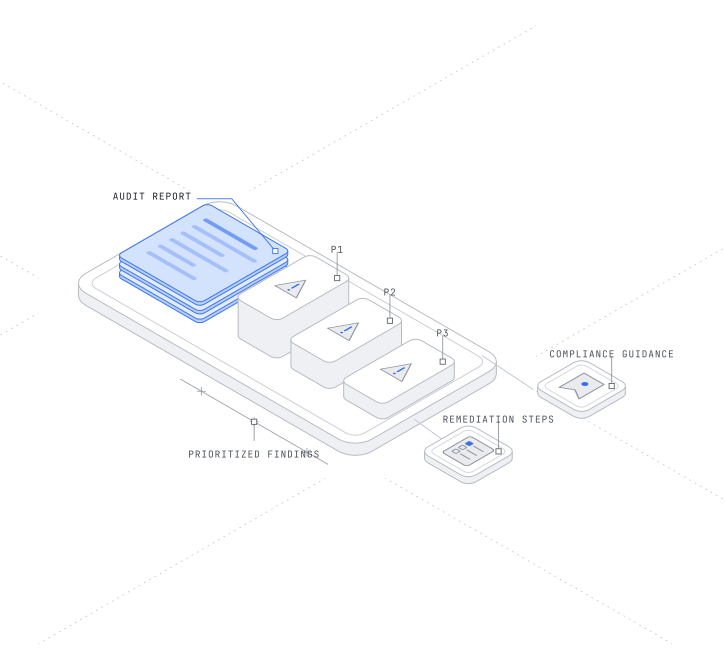
  4. Audit Reporting & Recommendations

    Turn Findings Into Fixes

    Deliver a detailed audit report with prioritized findings, actionable remediation steps, and guidance for compliance improvement.

    • Detailed audit report delivered to your team
    • Prioritized findings and remediation steps
    • Guidance for ongoing compliance improvement
    Talk to an Advisor
    Turn Findings Into Fixes

Next Steps

Where the Audit Leads Next

The audit verifies where your encryption stands, and its remediation guidance feeds the next round of your program.

FAQs

Frequently Asked Questions

Still have questions? Talk to our team

Scope Your
Audit

Tell us about your environment and deadlines, and we will come back with a scope, a timeline and a team.

Scope Your Audit