
PKI-as-a-Service
Enterprise PKIaaS
You Fully Own
Managed, compliant, quantum-ready private PKI, built and operated by dedicated cryptography experts.
Trusted by fastest growing
companies around the world.


Understanding Platform
The PKIaaS Difference
Every certificate authority runs on the same managed model, ensuring consistent ownership, compliance, and quantum readiness across your entire PKI.
You Own The CA
We build and manage your complete CA infrastructure, from deployment through monitoring, patching, and revocation, yet ownership of the CA and control of your keys never leave your organization.
Post-Quantum Ready
Issue hybrid and composite certificates that pair NIST-standardized ML-DSA with classical RSA or ECDSA, so algorithm transitions happen at the CA, never through a painful field-wide reissuance campaign.
Audit Ready by Default
Policy-driven workflows arrive preconfigured for NIST, HIPAA, PCI DSS, GDPR, FIPS, and eIDAS, producing a reviewed CP/CPS and full audit trails for every certificate.
Understanding Platform
Discover The Functionality of PKIaaS
The platform runs on a unified, high-availability architecture, ensuring consistent compliance and quantum readiness across every certificate you issue.
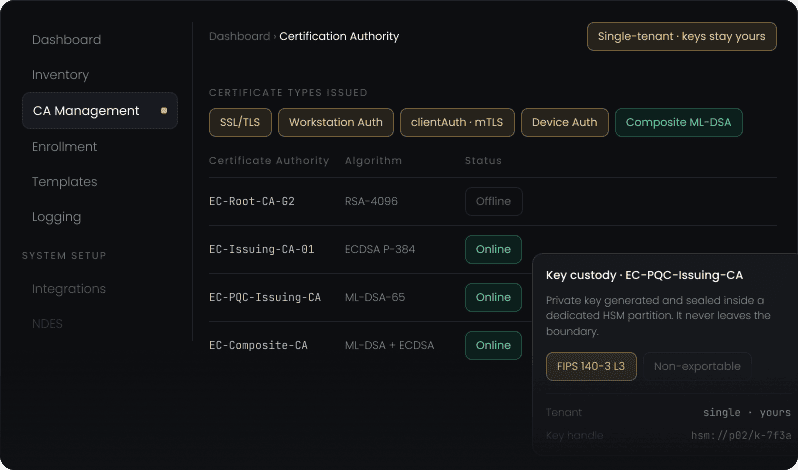
CA Management
Receive a fully managed, highly available, and compliant cloud CA infrastructure. Handle certificate issuance, enrollment, revocation, and renewal for all certificate types, including hybrid certificates, with redundancy built in.
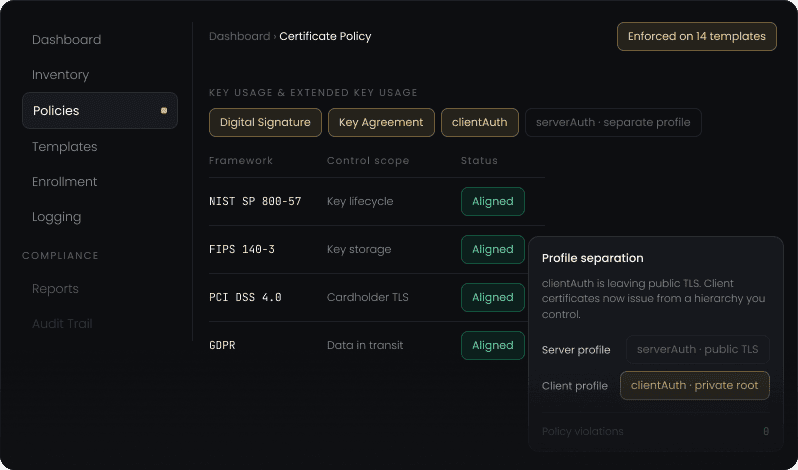
Policy Management
Define and enforce certificate policies, validity periods, and key usage rules across your organization. Integrate PQC capabilities and implement customizable certificate profiles with strict access controls.
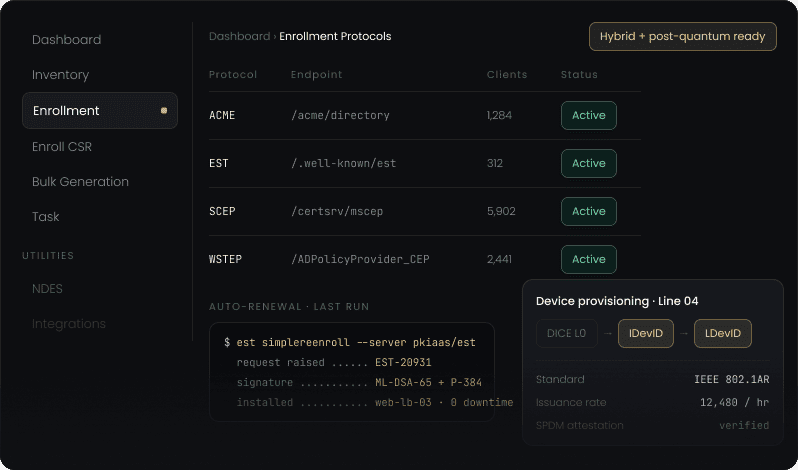
Automated Enrollment
Enable seamless certificate requests and installations through automated enrollment protocols. Support SCEP, WSTEP, EST, and ACME for streamlined issuance, enrollment, and renewal.
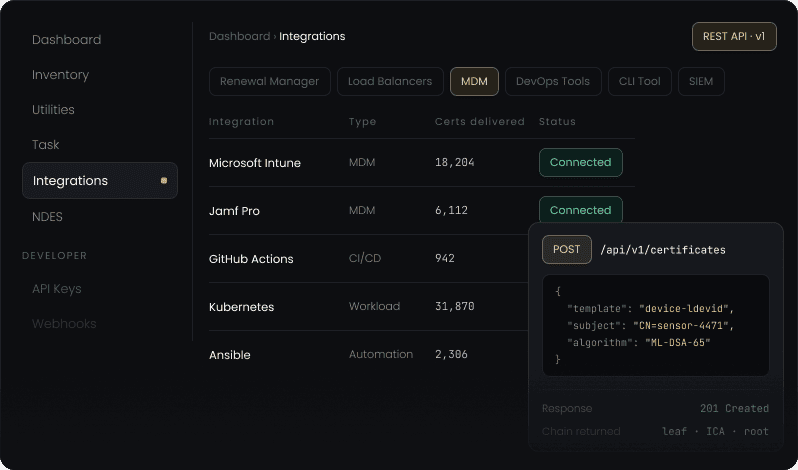
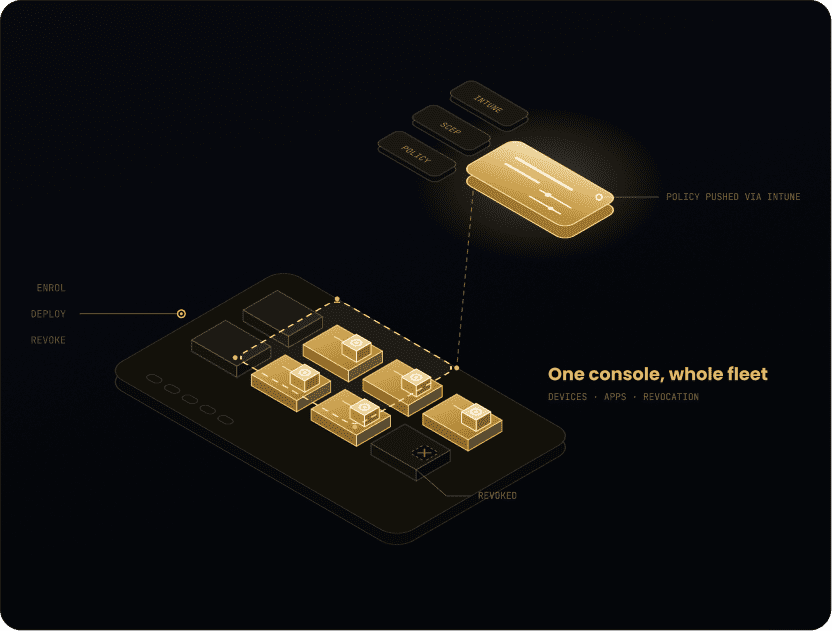
Mobile Device Management
Deploy high-assurance certificates through Microsoft Intune to secure devices and applications, with revocation and policy management automated. Certificate issuance for UEM and MDM platforms stays in sync in real time, with over-the-air enrollment and granular access control.
Expert Guidance on Demand
Dedicated PKI experts manage your security infrastructure end to end, including guidance through your post-quantum transition strategy, freeing your team to focus on core priorities.
Scalability & Flexibility
A high-availability, single-tenant architecture scales effortlessly across DevOps, cloud, and IoT environments, ready for hybrid certificates as your footprint grows.
Integrations
Seamless Advanced
Integrations
Effortlessly integrate PKIaaS into your existing infrastructure with support for SCEP, WSTEP, EST, and ACME enrollment protocols. From Microsoft Intune to enterprise identity and UEM/MDM platforms, PKIaaS issues and manages certificates across every environment you already run.
4
Enrollment Protocols
6
Compliance Frameworks
100+
Enterprises Secured
Use Cases
An Agent for Every Use Case
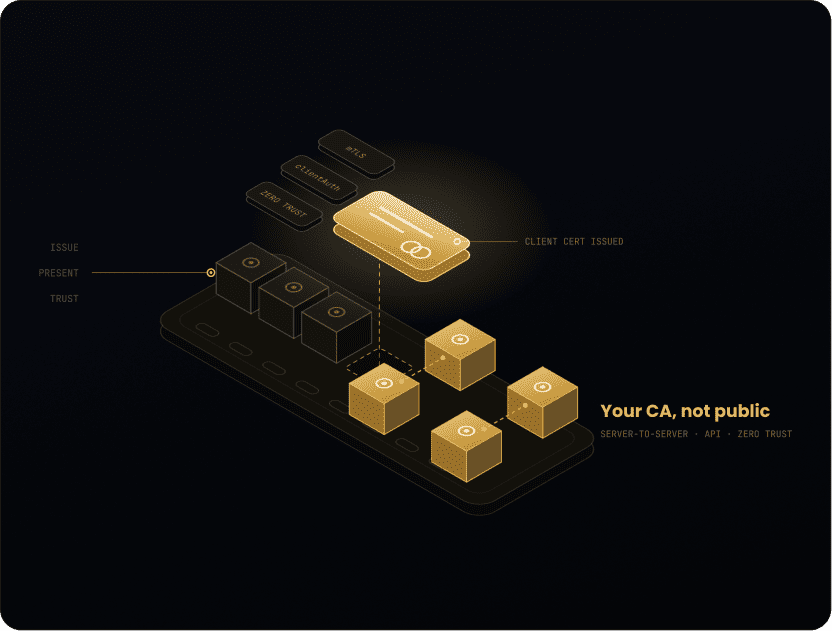
clientAuth & mTLS
Own the certificates public CAs are phasing out.
Issue client authentication and mutual TLS certificates as public CAs phase out clientAuth. Built for server-to-server, API, and zero trust workloads you control end-to-end.
Private CA Issued
Not dependent on a public CA's policy changes
Zero Trust Ready
Purpose-built for workload-to-workload auth
mTLS Native
Server-to-server and API traffic covered
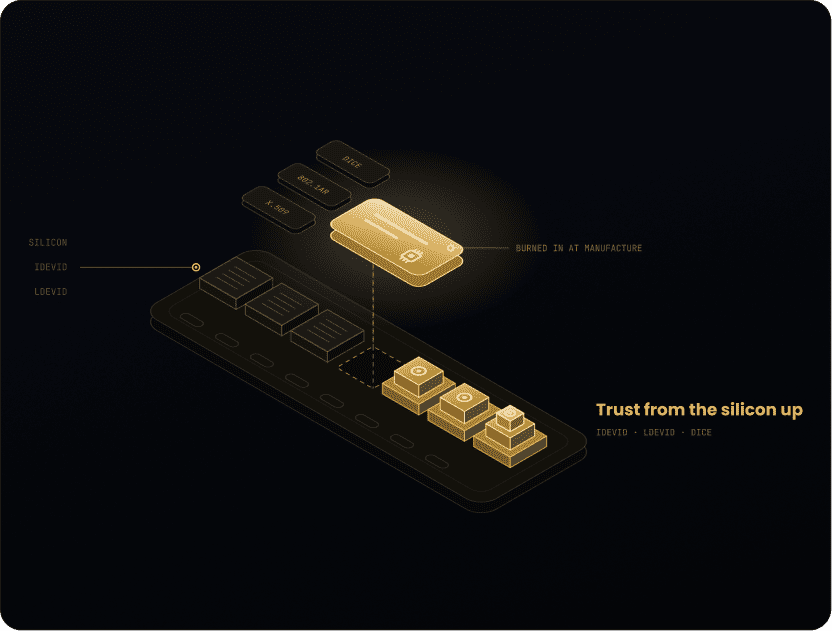
Hardware Identity
Trust built in at the silicon, not bolted on later.
Provision DICE and 802.1AR-compliant IDevID and LDevID certificates for chips and devices during manufacturing, establishing X.509 trust from the hardware up.
DICE & 802.1AR
Standards-compliant device identity
Manufacturing-Stage
Trust provisioned before deployment
Silicon to X.509
Hardware root of trust, extended
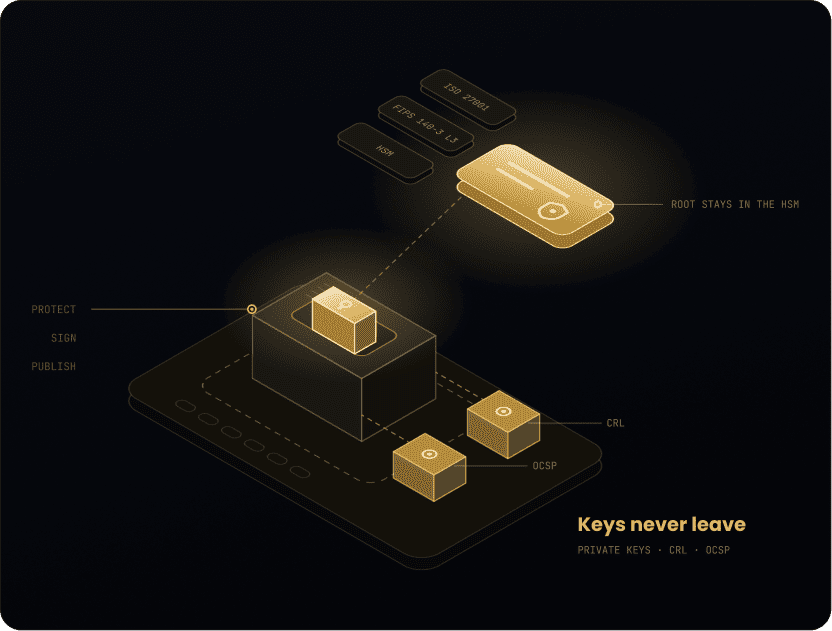
Managed Root CA
Your root, protected with the highest security.
Secure your root CA with ISO 27001 controls and FIPS 140-3 Level 3 HSMs, while you keep full control over private keys, CRL, and OCSP services.
ISO 27001 Controls
Enterprise-grade governance
FIPS 140-3 Level 3
HSM-backed key protection
Full Key Control
Ownership never leaves your hands
SPDM Attestation
Device identity at data center scale.
Supply device identity certificate chains for SPDM-enabled GPUs, NICs, SSDs, and accelerators, enabling authentication and firmware attestation across the data center.
SPDM-Enabled
GPUs, NICs, SSDs, accelerators covered
Firmware Attestation
Verified at boot, not assumed
Data Center Scale
Built for high-volume device fleets
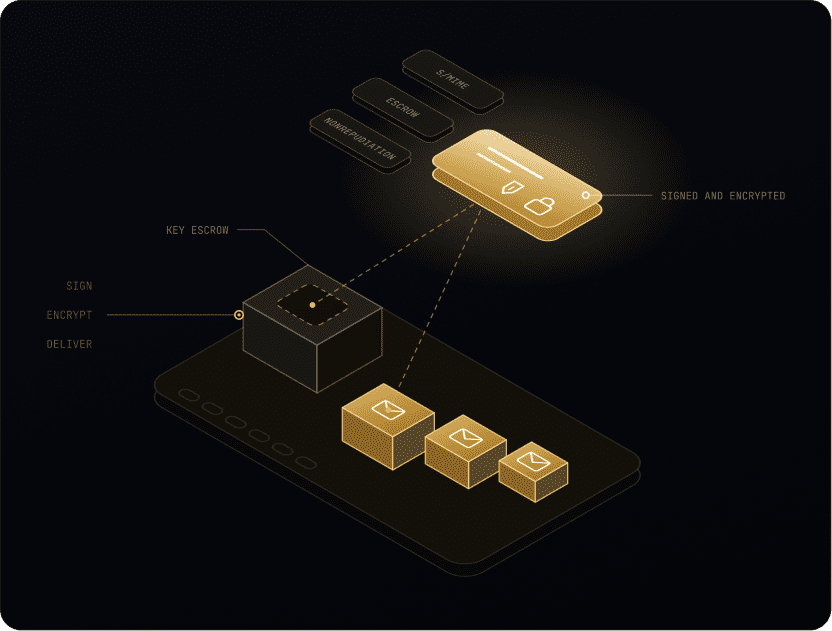
Secure Email
Signed, encrypted email that proves who sent it.
Deploy S/MIME for encrypted, signed email with automated key escrow, cross-platform compatibility, and non-repudiation that protects sensitive communications.
S/MIME Native
Encryption and signing, built-in
Automated Key Escrow
Recovery without the manual overhead
Cross-Platform
Works across mail clients and providers
Policy Governance
No certificate issues without your rules applied.
Restrict certificate issuance to authorized users and systems, and automatically enforce internal security policies and compliance frameworks, including PQC standards, for every certificate.
Access Restricted
Only authorized users and systems issue
Policy-Enforced
Every certificate checked automatically
PQC-Aligned
Post-quantum standards built into governance
Deployment Options
Deploy It Anywhere
You Operate
Choose the deployment model that aligns with your security, compliance, and operational goals, ensuring a seamless, high-assurance PKI experience.
On-Premises
Deploy PKI within your own infrastructure with a fully managed solution, maintaining full control while benefiting from expert guidance and PQC capabilities.
SaaS
Leverage cloud-based PKIaaS to establish secure digital identities without the complexity of managing infrastructure, reducing costs while enhancing security.
Managed PKIaaS
Get a fully customized, enterprise-grade PKI solution with expert management, robust compliance, and seamless scalability without the operational burden.
Try It Out Free Trial
Spin up PKI-as-a-Service free for 15 days. Stand up a fully managed, high-assurance PKI, issue certificates on demand, and scale trust across your environment. No hardware to buy.
Every Layer of Cryptography.
One Team to Secure It.
See how Encryption Consulting secures what your enterprise depends on, from assessment through deployment.
Request a Demo