A Strategy Built
for Your Clouds

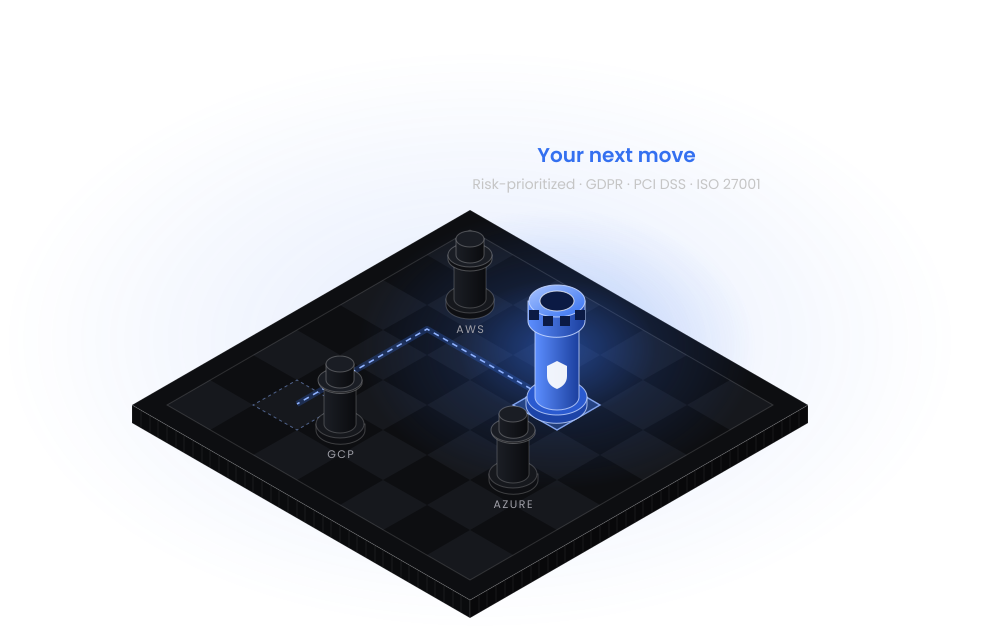
Encryption, tokenization, risk prioritization and compliance strategy for AWS, Azure and GCP, aligned to GDPR, PCI DSS and ISO 27001.

Trusted by fastest growing
companies around the world.

American Airlines logo
Centene Corporation logo
Intrado logo
NTT Data logo
Pfizer logo
FAB logo
Anheuser-Busch InBev logo
CBCInnovis logo
JCPenney logo
OU Health logo
Protegrity logo
Blue Cross Blue Shield logo
Dell Technologies logo
Lumen logo
P&G logo
nCipher logo
Builders FirstSource logo
Intel logo
Magella Health logo
Pega logo
LivaNova logo

Why Cloud Data Protection Strategy?

A Cloud Strategy You Can Act On

A tailored, actionable strategy that strengthens encryption, controls, and compliance, aligned to your risk posture and growth objectives.

Tailored Roadmaps illustration

Tailored Roadmaps

Develop a detailed plan customized to your cloud environment and your target security goals across every platform.

Data Protection Focus illustration

Data Protection Focus

Address data at rest, in transit, and in use with specialized approaches built for each state of your data.

Regulatory Alignment illustration

Regulatory Alignment

Ensure compliance with complex global standards, frameworks, and legal guidelines that apply to your business.

Scope

Five Domains, One Strategy

We design customized, risk-based cloud security strategies that advance your data security posture and align with your regulatory requirements.

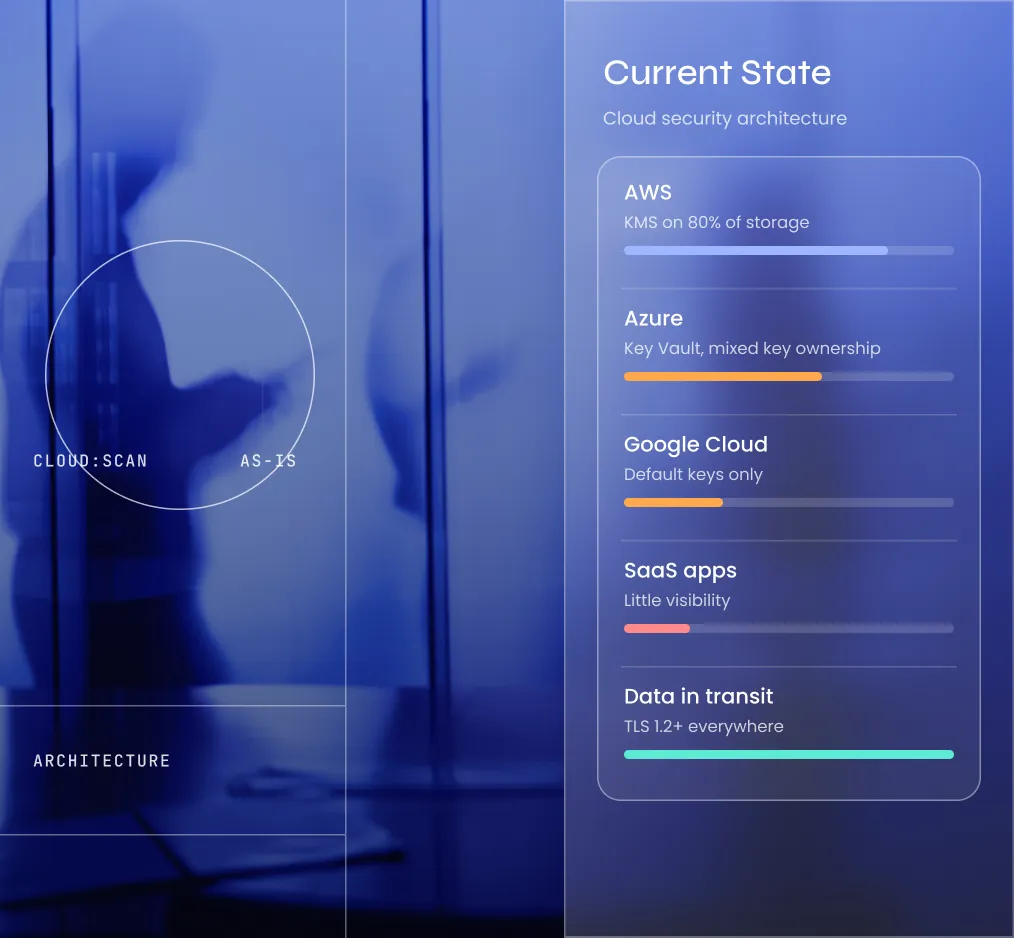
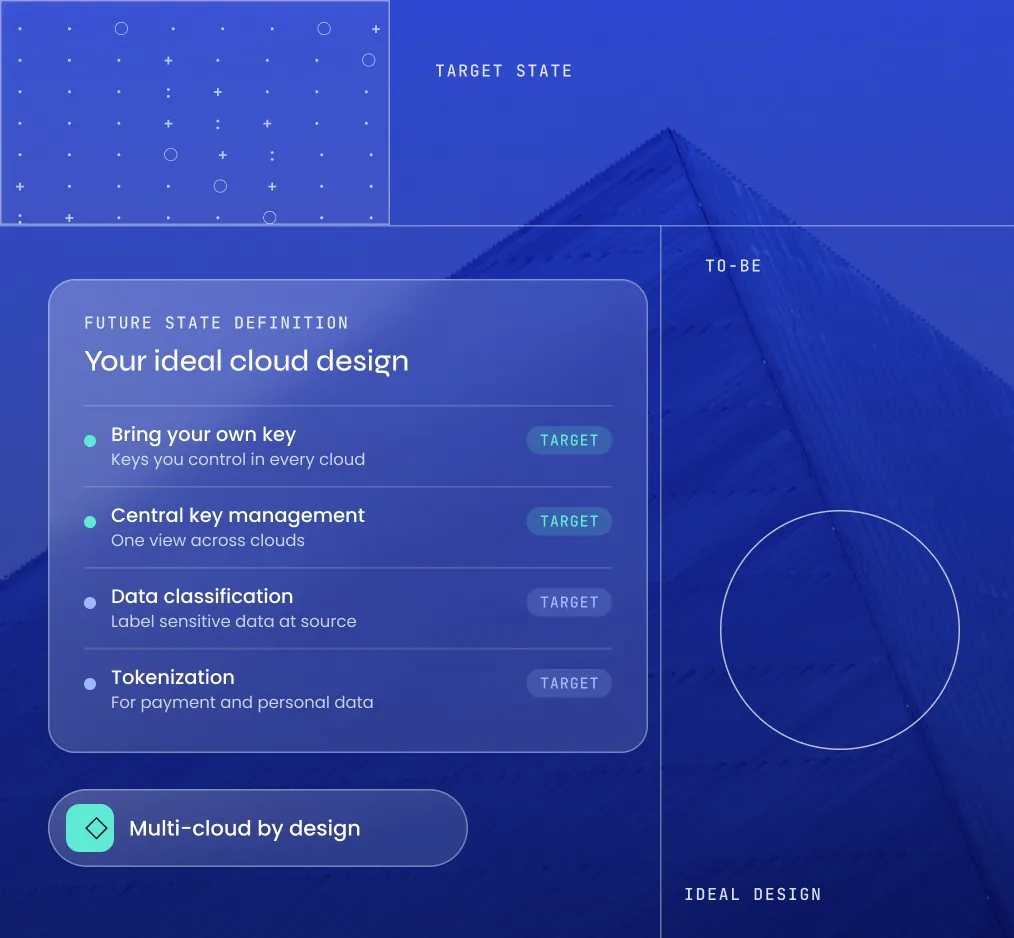
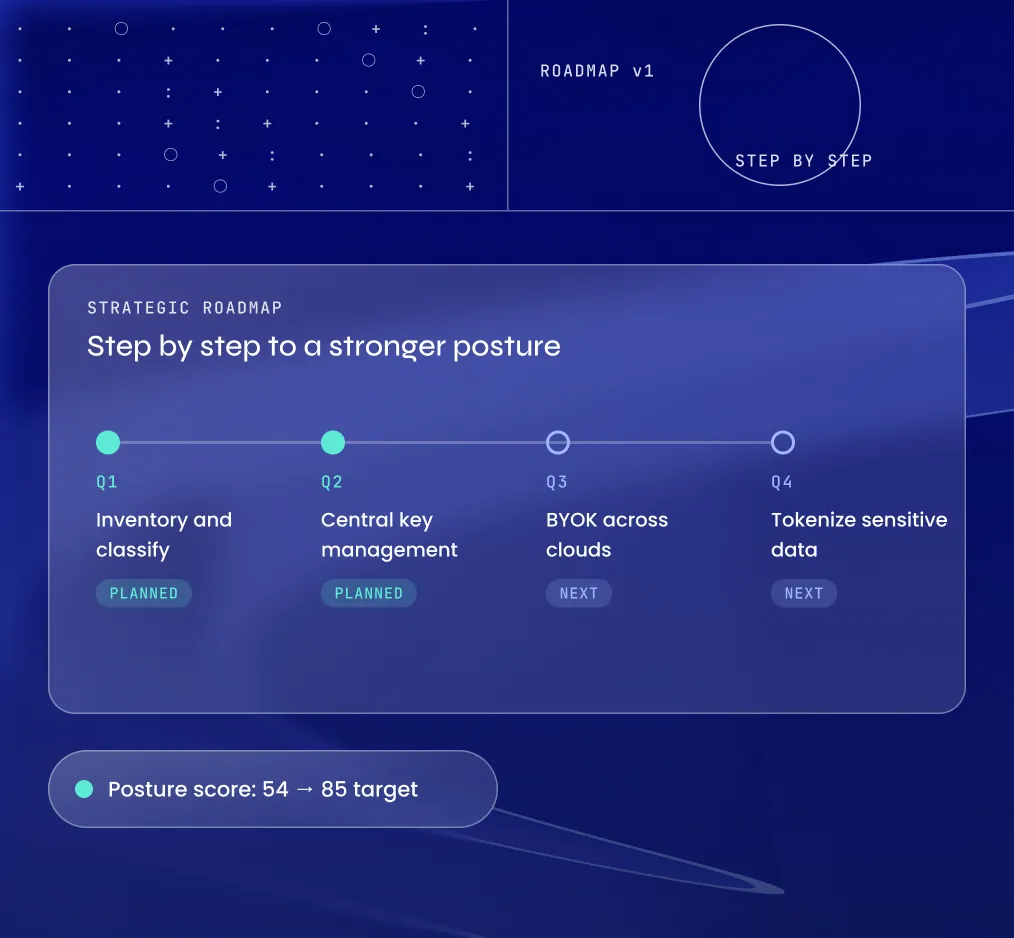
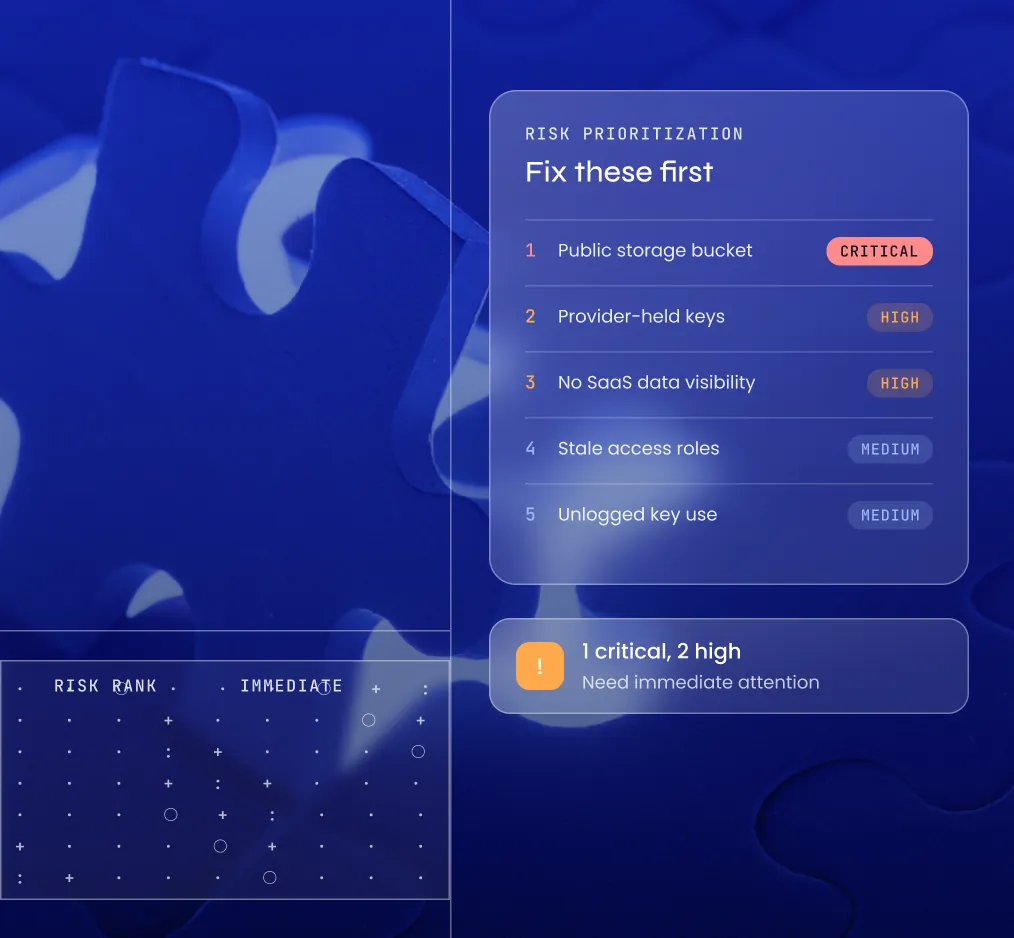
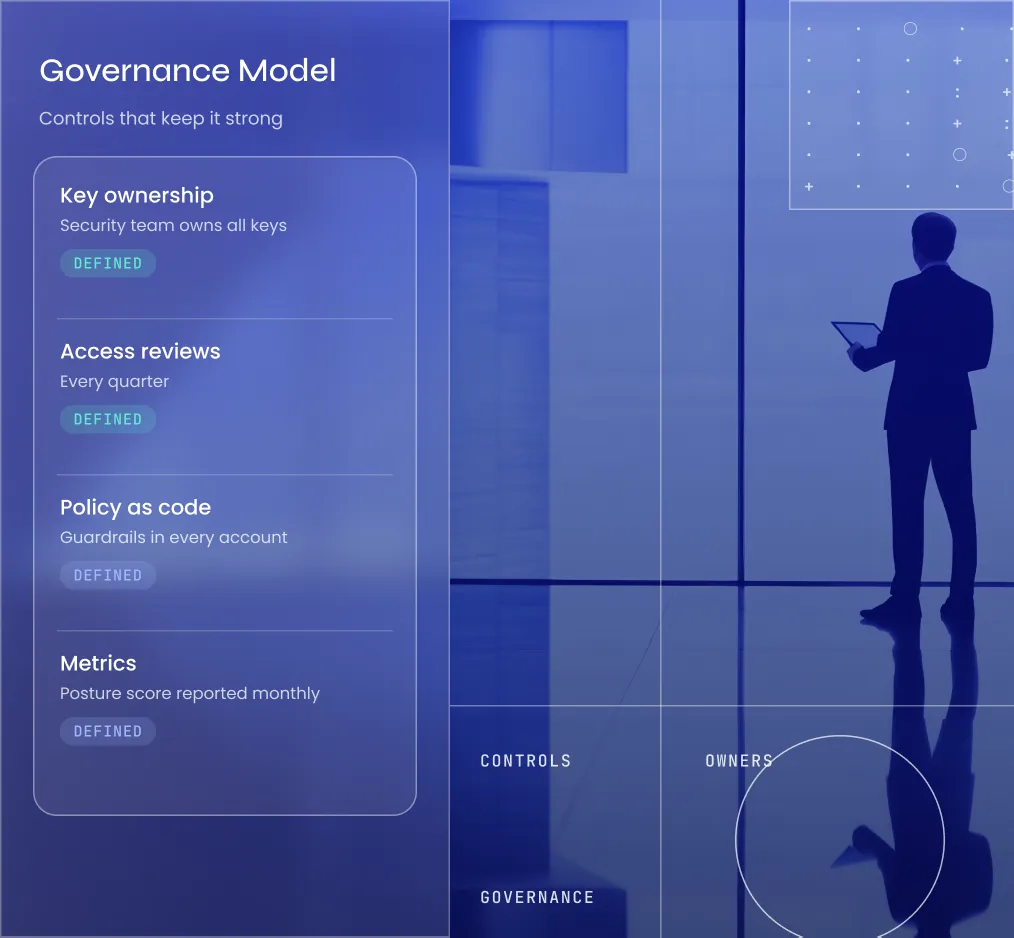
Current State Review Future State Definition Strategic Roadmap Risk Prioritization Governance Model
  1. Analyze your cloud security architecture to identify key gaps.

  2. Outline your ideal data protection design for cloud environments.

  3. Develop a step-by-step plan for security posture improvements.

  4. Highlight high-risk areas that need immediate security attention.

  5. Define controls to maintain a strong data security architecture.

Our Approach

Four Pillars of Your Cloud Strategy

A risk-prioritized strategy that meets regulatory standards while optimizing encryption, tokenization, and data governance initiatives.

  1. Tailored Strategy

    Fit the Plan to Your Cloud

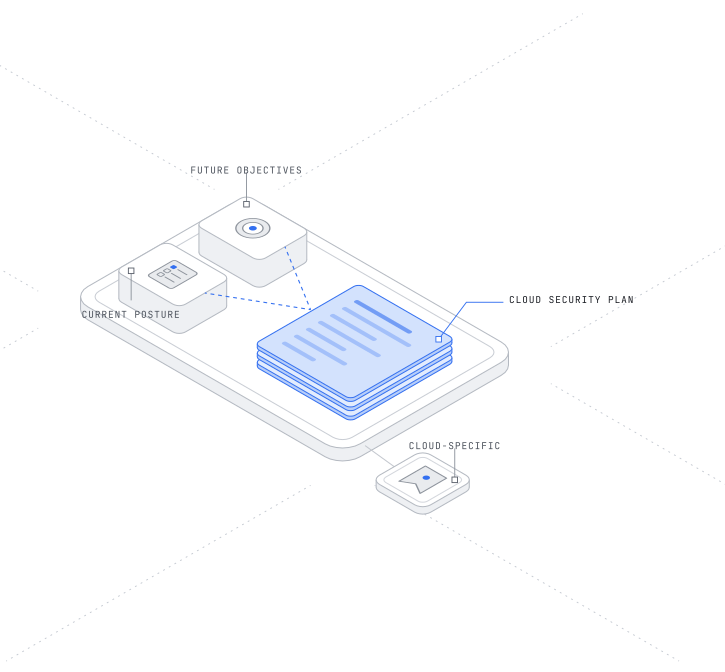
    Develop a cloud-specific security plan that aligns with your current posture and meets your future security objectives.

    • Cloud-specific security plan built for you
    • Aligned with your current posture today
    • Built for future security objectives
    Talk to an Advisor
    Fit the Plan to Your Cloud
  2. Maturity Roadmap

    Focus on What Counts

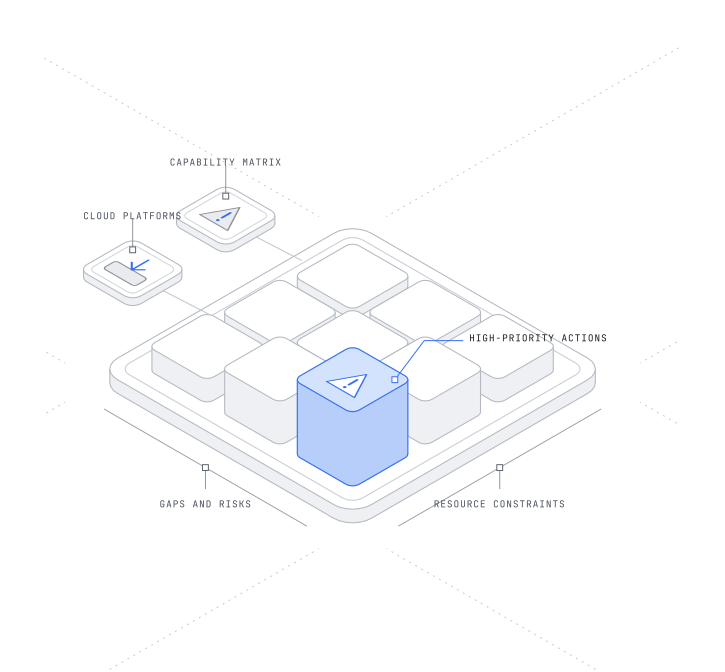
    Deliver a prioritized capability matrix based on your gaps, risks, and resource constraints across cloud platforms.

    • Prioritized capability matrix delivered
    • Based on gaps, risks, and resources
    • Effort focused on high-priority actions
    Talk to an Advisor
    Focus on What Counts
  3. Risk-First Focus

    Protect Sensitive Data First

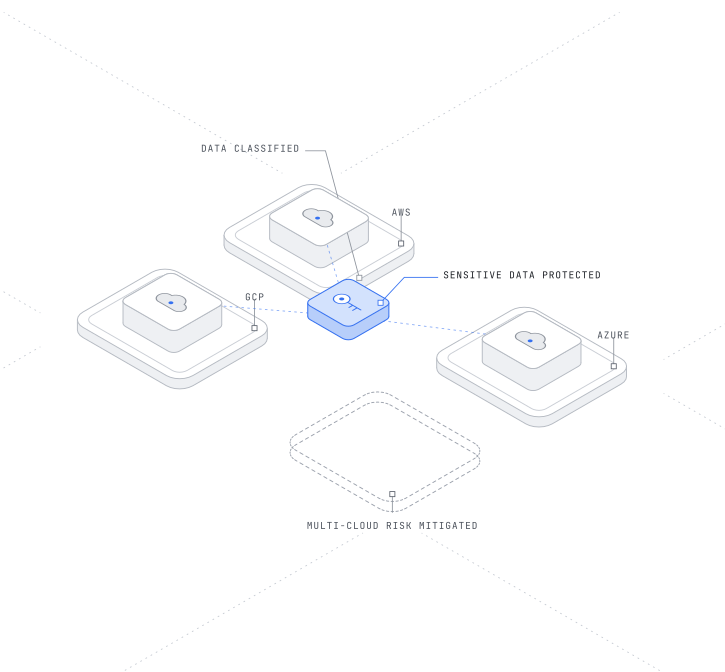
    Classify and protect sensitive data across your GCP, AWS, and Azure layers, mitigating risk in your multi-cloud setup.

    • Sensitive data classified across clouds
    • Protection across GCP, AWS, and Azure
    • Risks mitigated across multi-cloud setups
    Talk to an Advisor
    Protect Sensitive Data First
  4. Regulatory Readiness

    Align With the Regulations

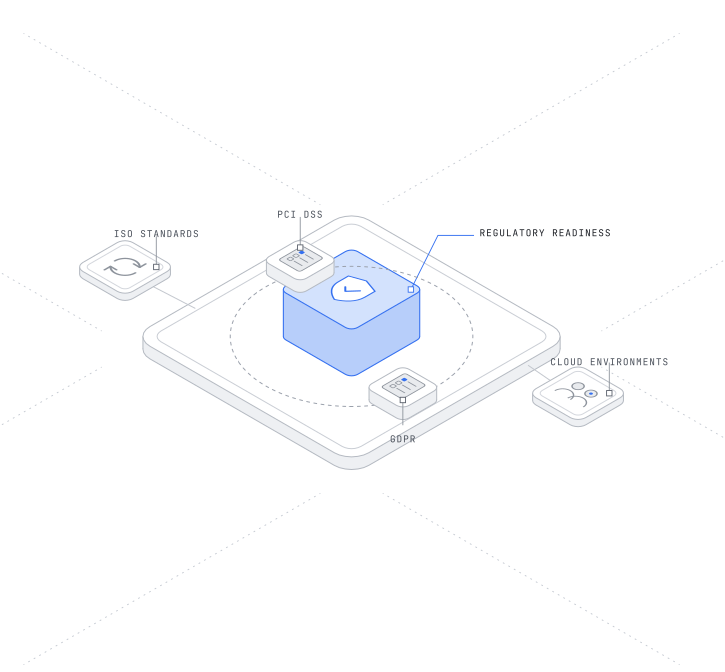
    Align strategies with GDPR, PCI DSS, and ISO standards so your cloud environments meet regulatory expectations.

    • Aligned with GDPR, PCI DSS, and ISO
    • Compliance addressed across the strategy
    • Cloud environments meet the standards
    Talk to an Advisor
    Align With the Regulations

Next Steps

Where the Strategy Leads Next

The strategy gives you a prioritized, actionable roadmap, and implementation turns it into working controls.

FAQs

Frequently Asked Questions

Still have questions? Talk to our team

Plan Your
Strategy

Tell us about your environment and deadlines, and we will come back with a scope, a timeline and a team.

Plan Your Strategy