Know Where Your
Cloud Data Is Exposed

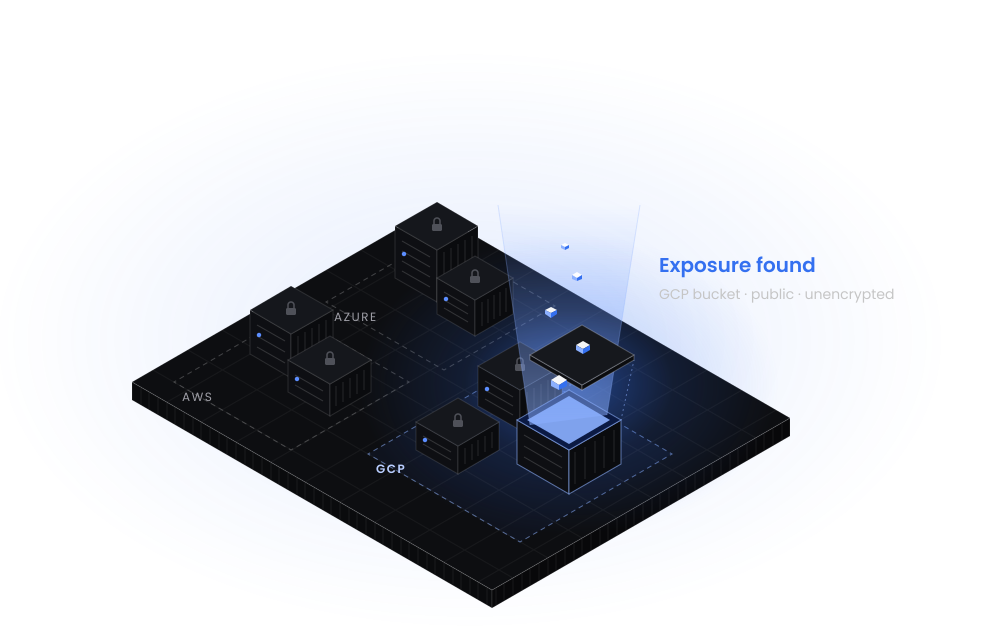
Asset discovery, risk gap analysis and compliance mapping for AWS, Azure and GCP, benchmarked against NIST, CIS and GDPR.

Trusted by fastest growing
companies around the world.

American Airlines logo
Centene Corporation logo
Intrado logo
NTT Data logo
Pfizer logo
FAB logo
Anheuser-Busch InBev logo
CBCInnovis logo
JCPenney logo
OU Health logo
Protegrity logo
Blue Cross Blue Shield logo
Dell Technologies logo
Lumen logo
P&G logo
nCipher logo
Builders FirstSource logo
Intel logo
Magella Health logo
Pega logo
LivaNova logo

Why Cloud Data Protection Assessment?

Clarity on Your Cloud Data Risk

A clear view of your cloud security gaps, benchmarked against industry standards, with prioritized steps to close them.

Current State Analysis illustration

Current State Analysis

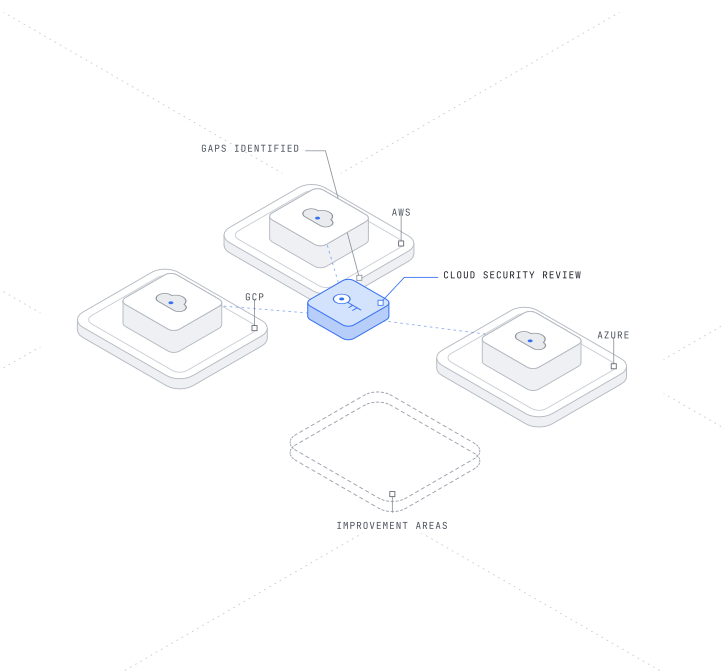
Evaluate your cloud environment to identify gaps and security improvement areas across AWS, Azure, and GCP.

Benchmark Alignment illustration

Benchmark Alignment

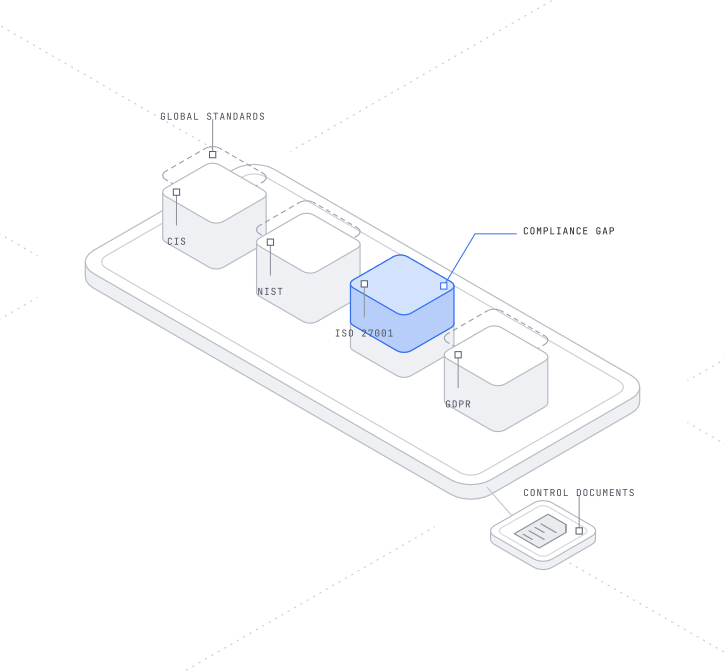
Benchmark control documents to ensure they meet NIST, CIS, ISO 27001, and GDPR standards across clouds.

Risk Clarity and Priority illustration

Risk Clarity and Priority

Get clarity on existing risks, with prioritized mitigation recommendations so your team knows where to start.

Scope

Five Domains, One Assessment

Our assessment identifies gaps in your cloud environments and strengthens your data security posture management across AWS, Azure, and GCP.

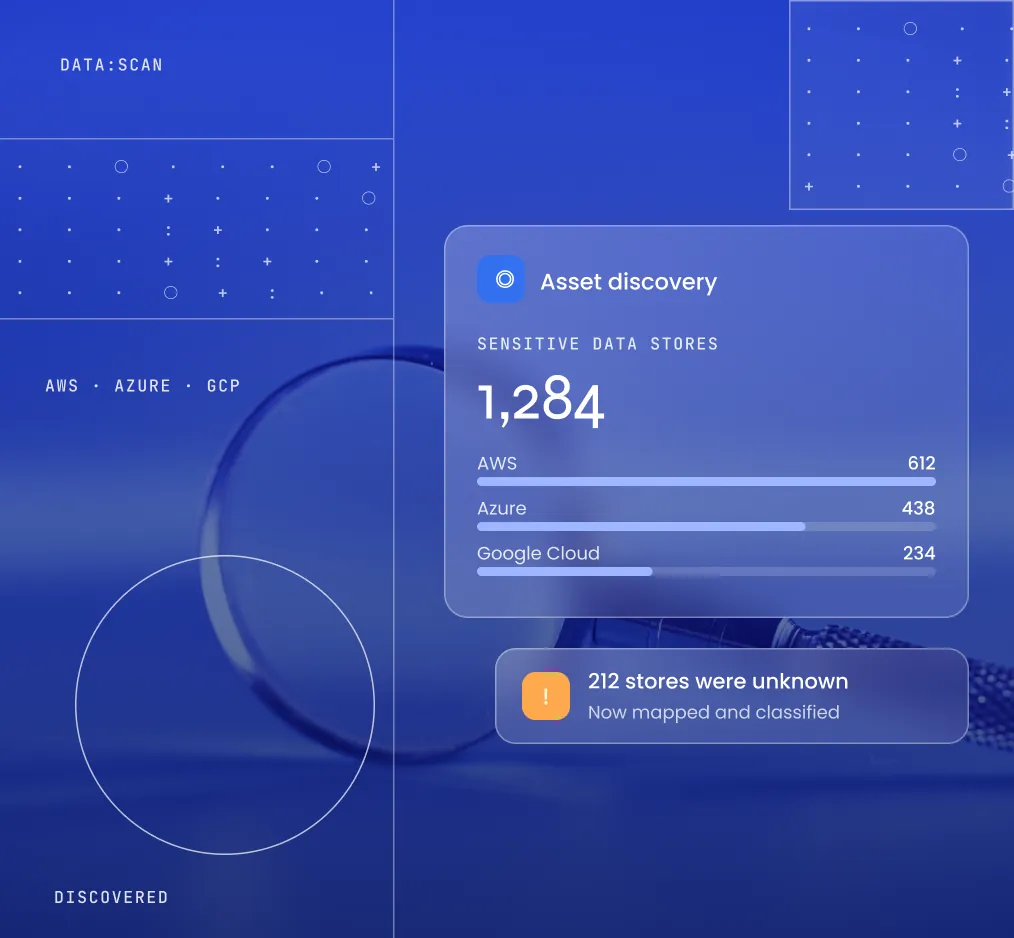
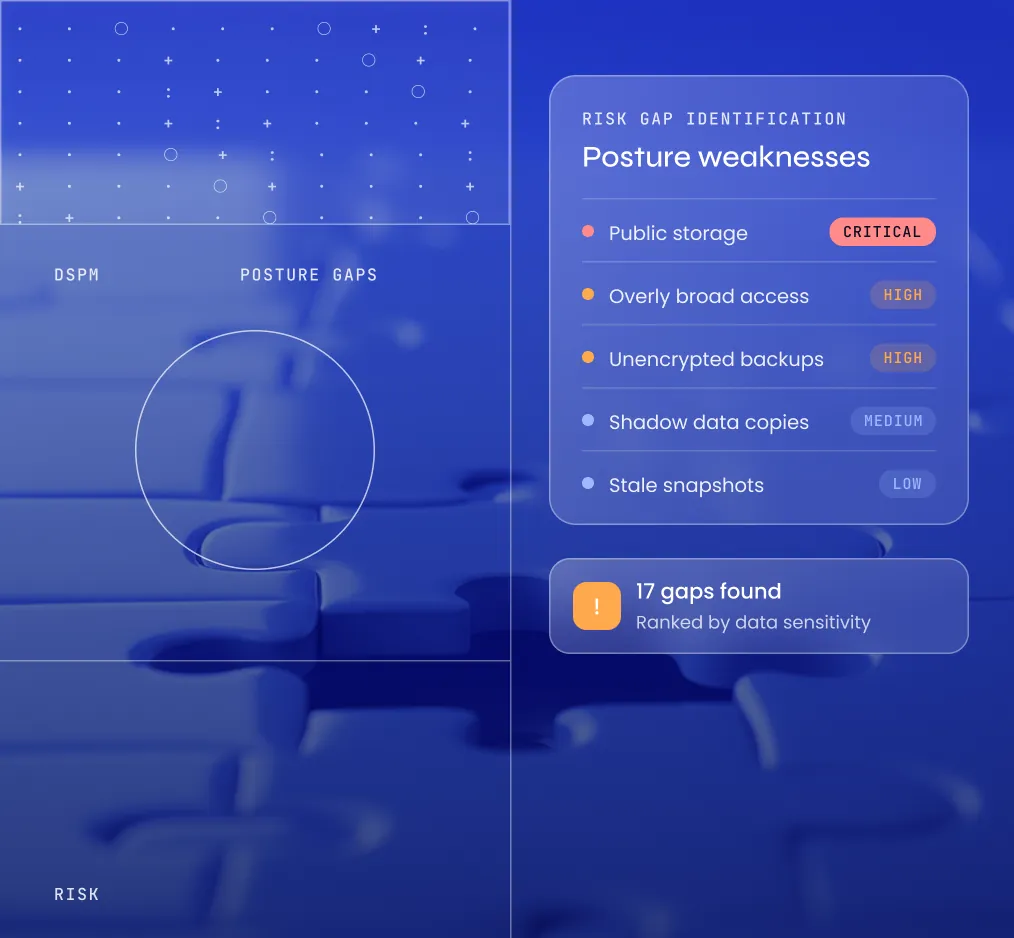
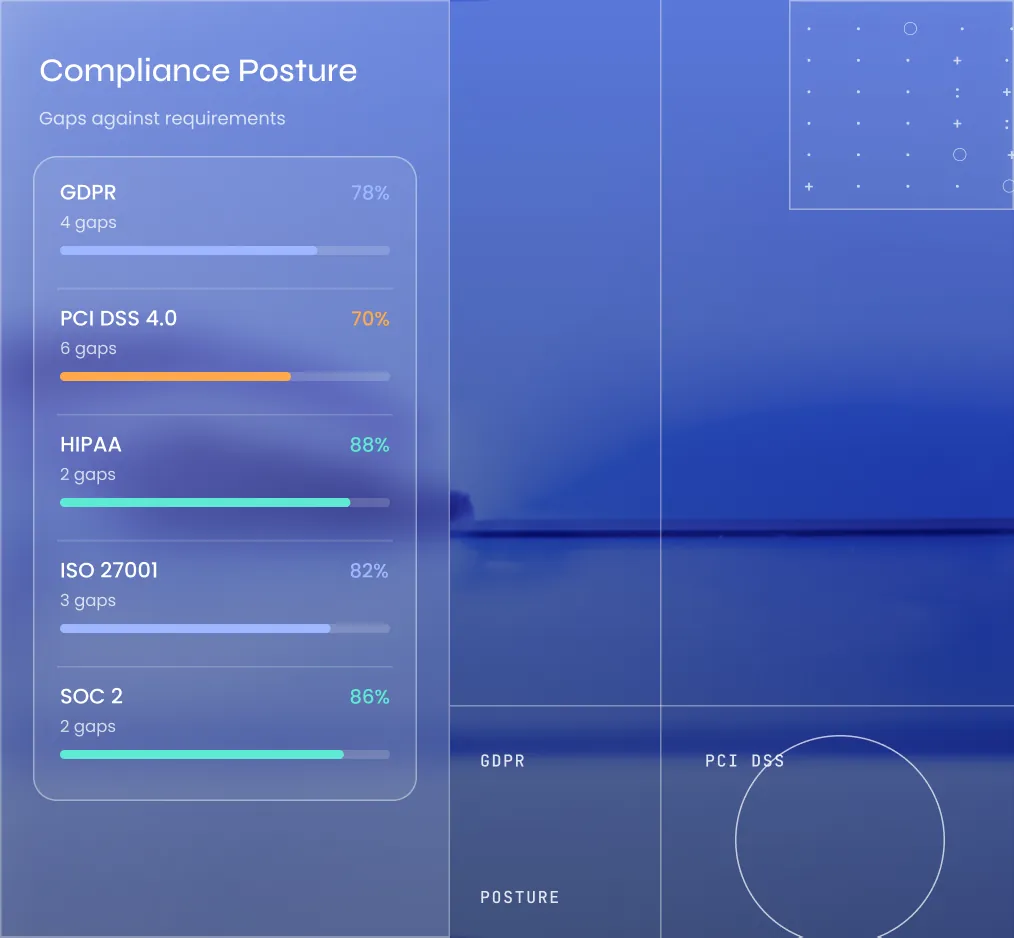
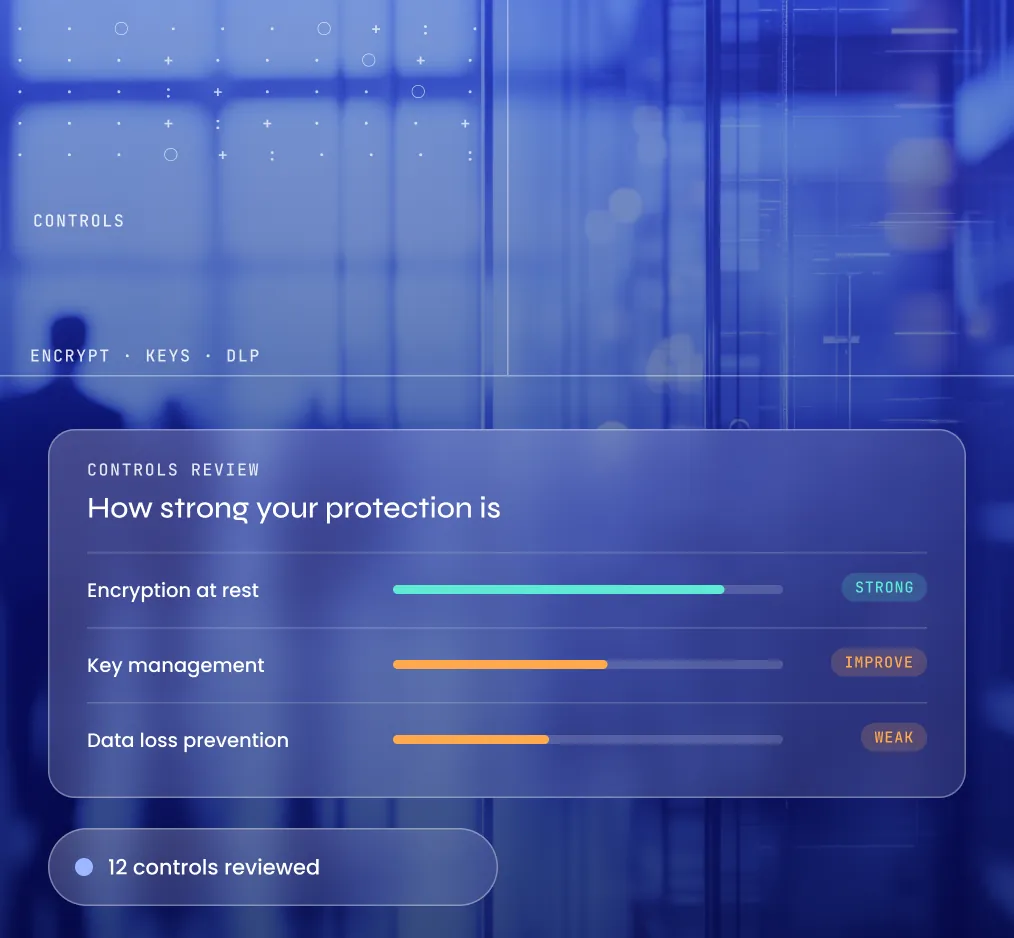
Asset Discovery Risk Gap Identification Compliance Posture Controls Review Remediation Advice
  1. Identify sensitive data locations across AWS, Azure, and GCP.

  2. Uncover weaknesses affecting your data security posture management.

  3. Analyze compliance gaps against GDPR, PCI DSS, and other requirements.

  4. Evaluate encryption, key management, and protection capabilities.

  5. Deliver actionable steps to strengthen your data protection.

Our Approach

Four Pillars of Your Cloud Assessment

A detailed evaluation of your cloud environment, strengthening data security posture through discovery, risk analysis, and prioritized actions.

  1. Comprehensive Review

    Review Every Cloud You Run

    Assess your cloud security environment across AWS, Azure, and GCP to find gaps and improvement areas in each platform.

    • AWS, Azure, and GCP fully covered
    • Cloud security environment assessed
    • Gaps and improvement areas identified
    Talk to an Advisor
    Review Every Cloud You Run
  2. Standards Alignment

    Benchmark Against the Standards

    Benchmark your data security posture against CIS, NIST, ISO 27001, and GDPR to meet global regulatory expectations.

    • Posture benchmarked against CIS and NIST
    • Control documents checked as well
    • Regulatory requirements fully addressed
    Talk to an Advisor
    Benchmark Against the Standards
  3. Risk Prioritization

    Know What to Fix First

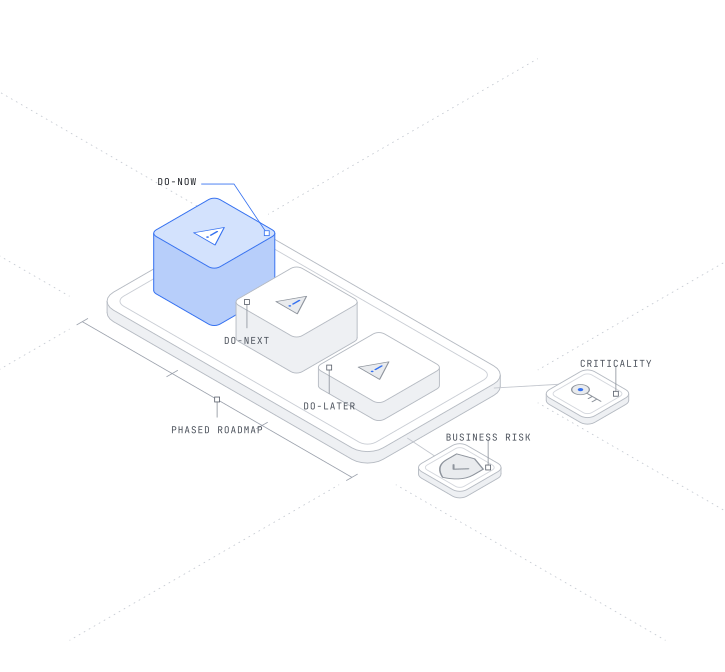
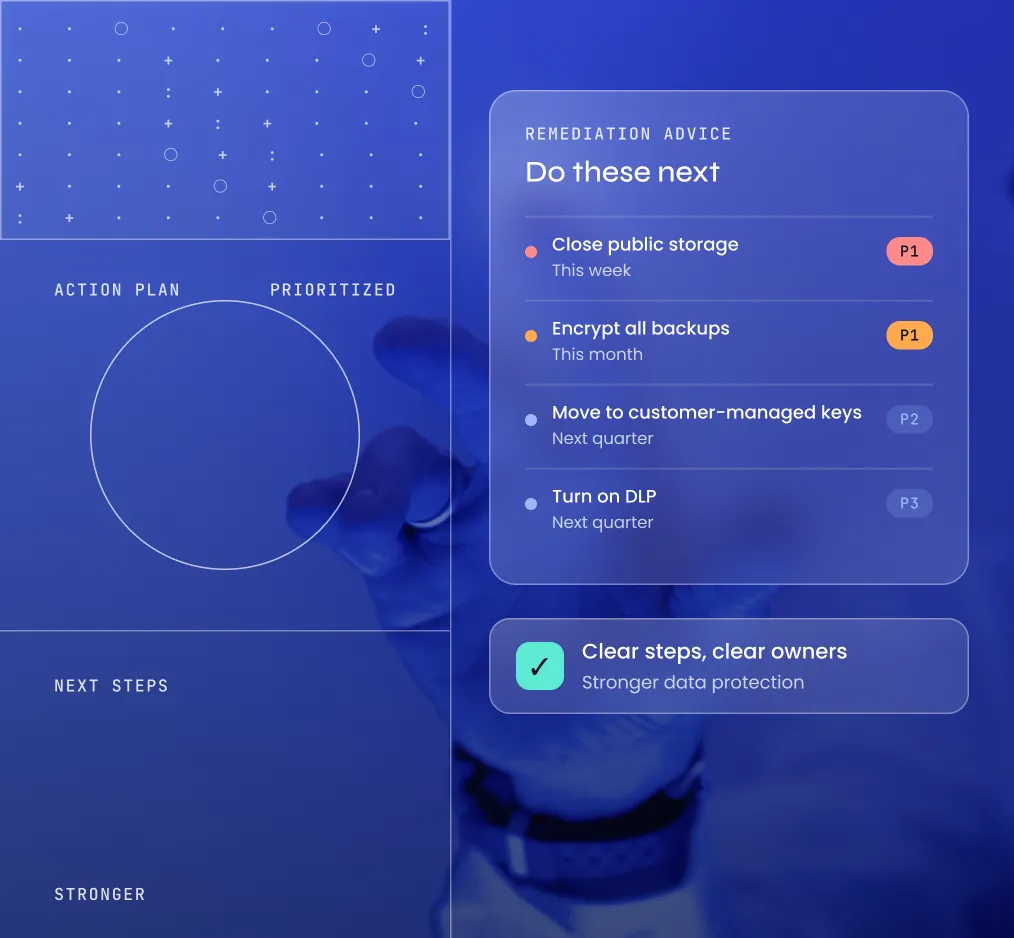
    Identify Do-Now, Do-Next, and Do-Later actions based on criticality and business risk for immediate improvement.

    • Do-Now, Do-Next, Do-Later actions set
    • Phased roadmap based on business risk
    • Faster progress on urgent improvements
    Talk to an Advisor
    Know What to Fix First
  4. Clear Documentation

    Put It in Writing

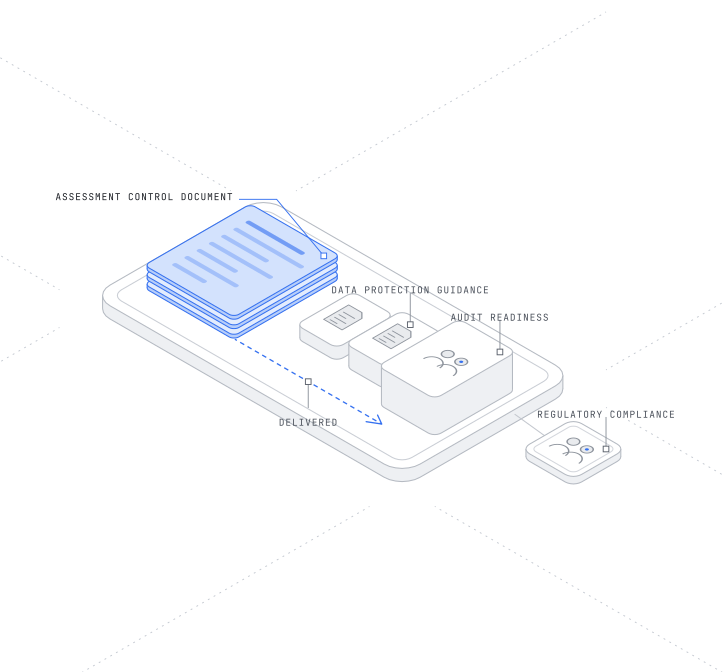
    Receive an Assessment Control Document that guides your data protection and regulatory compliance needs for audits.

    • Assessment Control Document delivered
    • Guidance for data protection needs
    • Guidance for regulatory compliance needs
    Talk to an Advisor
    Put It in Writing

Next Steps

Where the Assessment Leads Next

The assessment gives you prioritized actions and a remediation roadmap, and each cloud service that follows builds on it.

FAQs

Frequently Asked Questions

Still have questions? Talk to our team

Scope Your
Assessment

Tell us about your environment and deadlines, and we will come back with a scope, a timeline and a team.

Scope Your Assessment