
CodeSign Secure
Secure Your Code
With Confidence
Protect your software with a powerful, policy-driven code-signing solution to streamline security effortlessly.
Trusted by fastest growing
companies around the world.


Understanding Platform
The CodeSign Secure Difference
Every signing action runs through the same policy engine, ensuring consistent, verifiable control across every platform you sign for.
Quantum-Ready by Design
One of the first enterprise code signing platforms to ship native PQC support, with MLDSA and LMS algorithms built in, so your signing infrastructure is prepared before the threat arrives.
Policy-First Architecture
Every signing action is governed by RBAC, M-of-N quorum approvals, and key-level restrictions enforced natively, not bolted on.
HSM-Grade Key Protection
FIPS 140-3 Level 3 HSM enforcement ensures private keys never leave secure hardware, regardless of your deployment model.
Understanding Platform
Discover The Functionality of CodeSign Secure
Every signing action runs through the same policy engine, ensuring consistent, verifiable control across every platform and pipeline you ship from.
Policy-Driven Code Signing
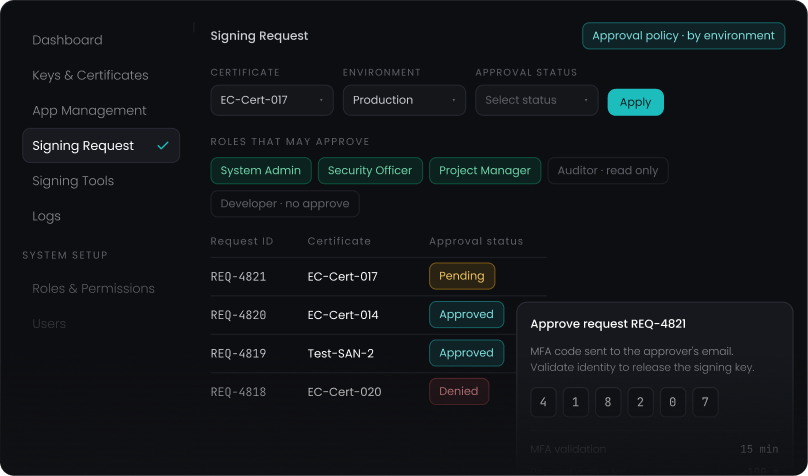
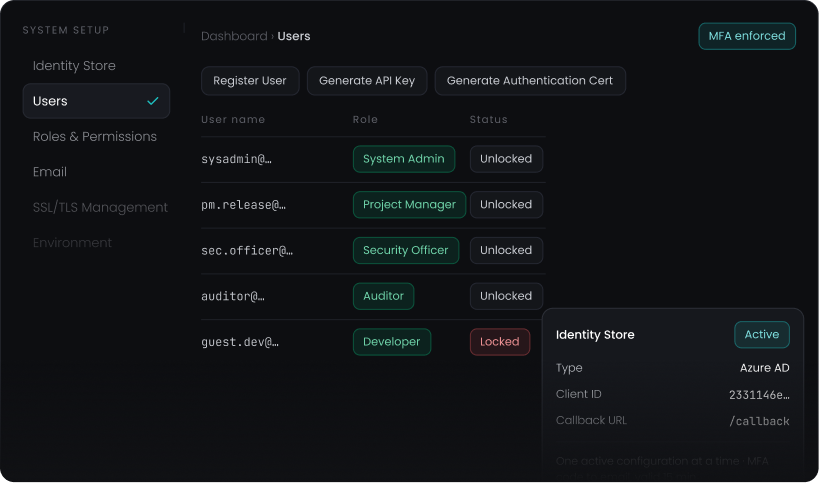
Secure your software pipeline with strict policy enforcement and controlled key access. Restrict who can sign, when, and with which keys, and implement RBAC and M-of-N quorum approvals to prevent unauthorized access.
Seamless CI/CD Automation
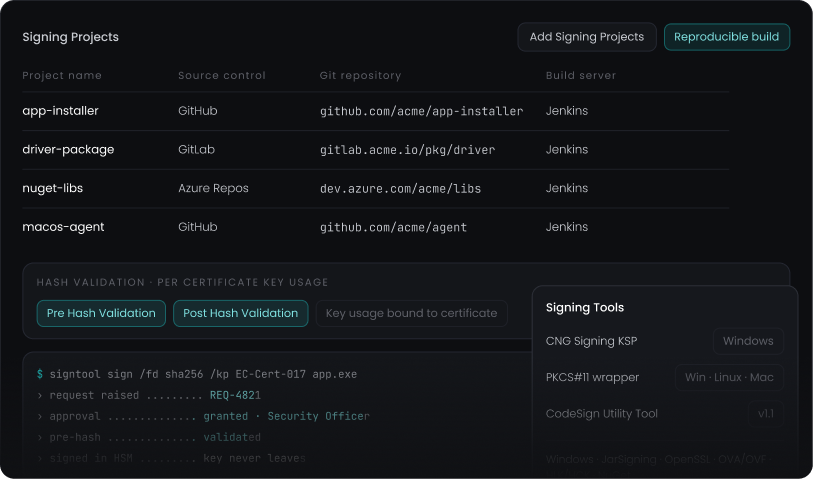
Embed secure code signing into DevOps workflows without disrupting agility. Automate signing within Jenkins, GitHub Actions, GitLab, Azure DevOps, and CircleCI, and enforce release checks that stop unsigned code before it reaches production.
Complete Auditability and Compliance
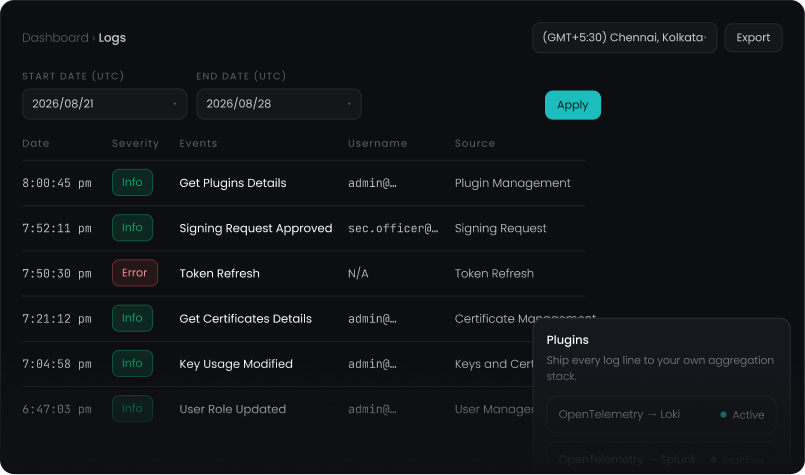
Gain real-time visibility into every code signing activity. Maintain detailed event logs and audit trails to track key usage, investigate incidents, and meet compliance, with centralized tracking and instant alerts on unauthorized attempts.
Trusted Time-Stamping
Anchor every signature to the moment it was made, so your software stays trusted even after the signing certificate itself has expired, regardless of how the signing command is executed.
HSM-Protected Signing Keys
Keep private keys in FIPS-certified hardware security modules, never exposed to the signing environment itself, for the highest level of key security and control.
Multi-Platform Coverage
Sign once from a single policy engine that spans Windows, macOS, Linux/RPM, Docker, Firmware, and OVA/OVF, so your security posture stays consistent as your stack grows.
Integrations
Seamless Advanced
Integrations
Explore the most connected code signing ecosystem with CodeSign Secure, integrating with your existing tools and platforms to simplify and secure the entire signing process. From DevOps pipelines to HSMs, cloud platforms to native signing tools, CodeSign Secure ensures airtight security, compliance, and automation at every stage.
40+
Integrations
3x
Faster Deployment
100+
Enterprises Secured
Use Cases
An Agent for Every Use Case
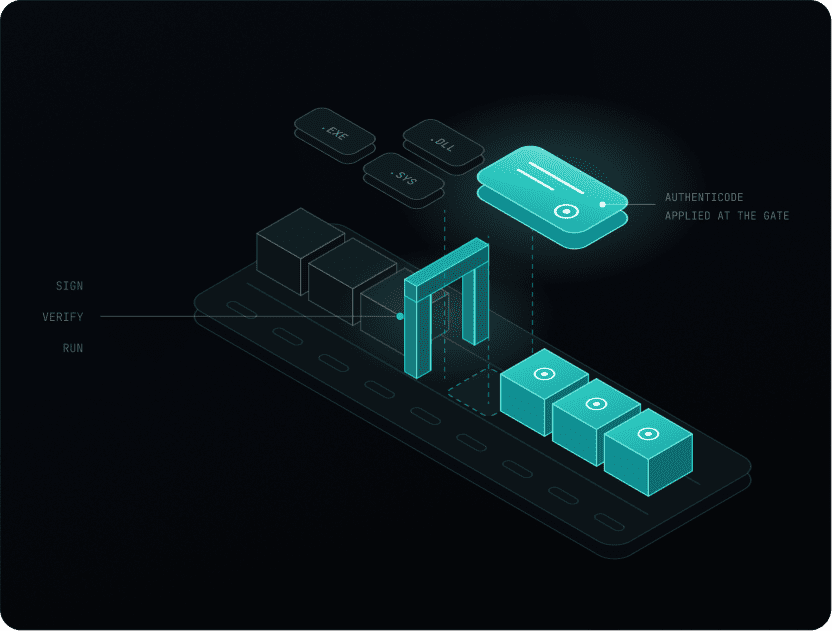
Windows Signing
Only trusted code runs. Everything else gets blocked.
Sign Windows executables and drivers to ensure only trusted code runs, reducing malware risks. Integrate seamlessly with Microsoft's infrastructure while ensuring compliance and user trust.
EXE & Driver Signing
Executables and kernel drivers, both covered
Microsoft-Ready
Built for Microsoft's signing infrastructure
Malware Defense
Untrusted binaries never run
Docker Image Signing
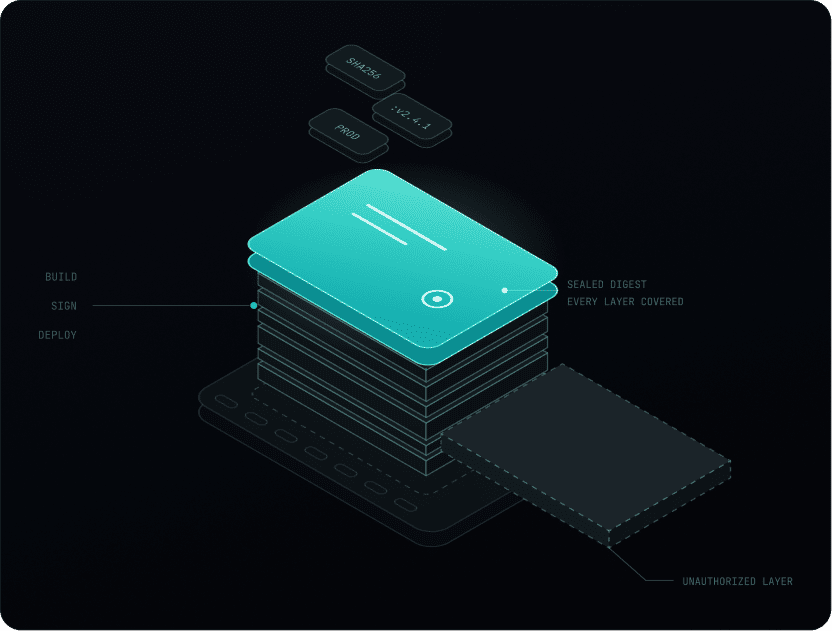
Immutable signatures for every container you ship.
Protect containerized applications with immutable digital signatures to prevent unauthorized modifications. Meet compliance while enabling secure deployments in production environments.
Immutable Signatures
Tampering is always detectable
Production-Grade
Built for container scale
Compliance-Ready
Audit requirements, met by default
Firmware Code-Signing
Secure the layer nothing else can patch later.
Secure firmware signing keys with HSMs to prevent unauthorized access. Ensure only trusted firmware loads at startup, reducing supply chain risks and improving system security.
HSM-Protected Keys
Never leave secure hardware
Trusted Boot
Only verified firmware loads
Supply Chain Defense
Closes a hard-to-patch gap
Apple Signing
Distribute with confidence across every Apple platform.
Sign macOS apps to enable secure distribution. Prevent malware, enhance user trust, and ensure compliance with Apple's security requirements.
Full Platform Coverage
Native support for macOS apps
User Trust
No security warnings on install
Apple-Compliant
Meets Apple's own standards
Linux/RPM Signing
Package integrity, verified before install.
Sign Linux RPM packages to prevent unauthorized modifications. Ensure seamless verification by package managers, improving software trust, security, and compliance.
RPM Signing
Native Linux package support
Package Manager Verified
Validated automatically
Modification Detection
Unauthorized changes flagged
OVA/OVF Code-Signing
Tamper-proof virtual machines, every time.
Digitally sign OVA/OVF files to prevent tampering and ensure secure deployments. Simplify compliance while maintaining integrity across virtualization platforms.
OVA/OVF Signing
Both formats, one workflow
Cross-Platform
Works across major hypervisors
Deployment Integrity
Confirms nothing was altered
Deployment Options
Deploy it anywhere
you build
Deploy CodeSign Secure in the environment that best fits your build pipeline, security, and operational needs.
On-Premises
Deploy CodeSign Secure on your infrastructure, using physical or virtualized servers, with private keys securely stored in an existing or newly configured HSM.
Cloud
Run CodeSign Secure on containers hosted in AWS, Azure, or private cloud environments, with seamless cloud HSM integration for secure key management.
SaaS
Leverage a fully managed, cloud-hosted solution with built-in HSM security, offering all on-premises features via API access without the complexity of infrastructure management.
Hybrid
Deploy on-premises using containers or physical servers while securely managing private keys in cloud HSMs, on-prem HSMs, or both for maximum flexibility.
Try It Out Free Trial
Experience CodeSign Secure free for 15 days. Sign code, containers, and artifacts with HSM-protected keys, and enforce signing policies across every CI/CD pipeline. Up and running in minutes.
Every Layer of Cryptography.
One Team to Secure It.
See how Encryption Consulting secures what your enterprise depends on, from assessment through deployment.
Request a Demo